So, there’s a nasty little Ursniff campaign going around. Emails containing password protected zip files, with the password in the body of the email. Every single one I’ve seen has the same password (123456). Very creative, right?
Anyway, the zip contains a malicious document file with some more or less obfuscated macros. I pulled a chunk of heavily obfuscated powershell out of one of the macros, so let’s go through deobfuscating it.

So, you can see we start with some base64 encoded stuff…let’s go to CyberChef.
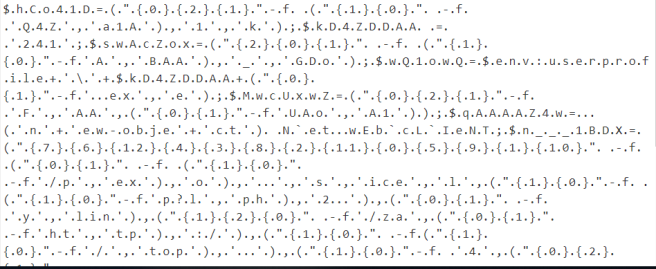
Here, we select the “from base64” option, and get some very ugly text. We can clean it up a little by converting to hex, removing null characters, then converting back from hex.
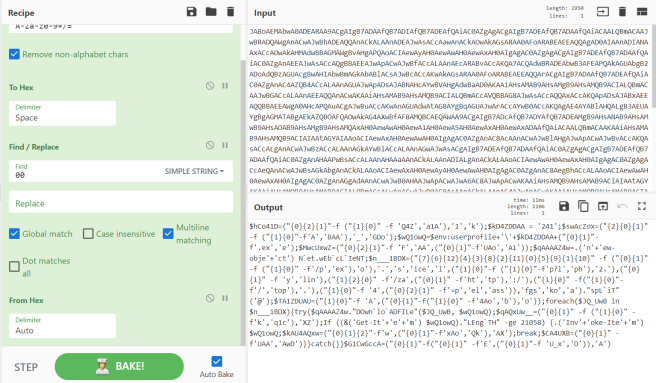
Now, it’s cleaned up a bit, but still ugly as sin.
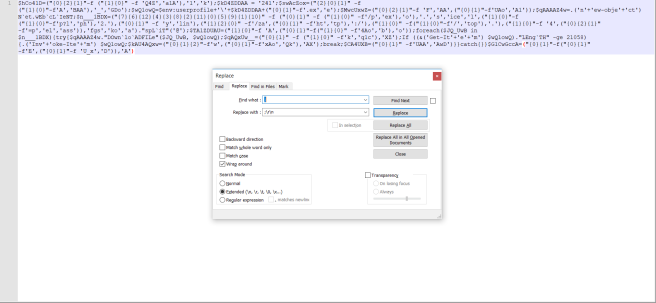
So…we’ll put it into notepad++, find instances of “;” and replace with \r\n (carriage return > newline) to separate it into workable chunks.
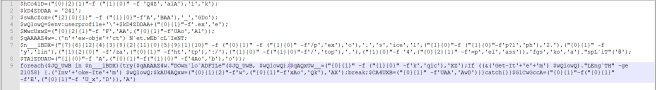
Now we can see that the first 8 lines are each variable declarations, and the last is a foreach statement containing “invoke item.” Now…I don’t want to invoke anything, but I do want to know how those variables decode. I could, of course, manually deobfuscate them, but that sounds like work, and if you’ve ever met me, you’ll know I’m all about working smarter, not harder…so let’s have powershell do the work for us. We’ll just paste each variable declaration into powershell, then we can just run the variable and it will spit out the decoded text.
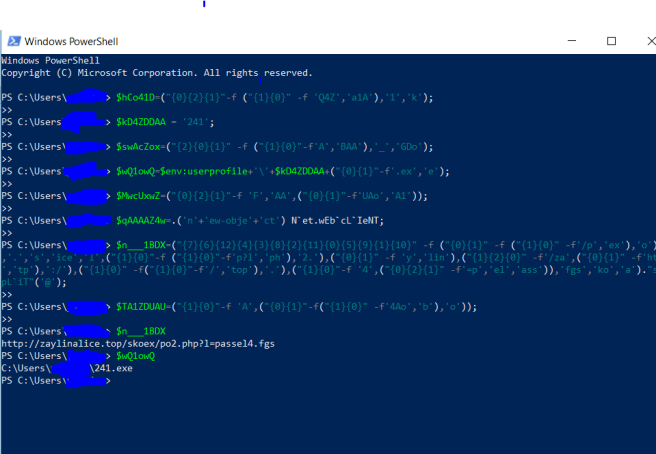
Now…we can see that the $n___1BDX variable contains a URL to download a payload from (zaylinalice[.]top/skoex/po2.php?1=passe14.fgs), and the $wQ1owQ variable contains the path and filename to store the payload as (%userprofile%\241.exe).
Now…this is nothing fancy…just wanted to make the point that you always have a choice between spending inordinate amounts of time manually deobfuscating things or just letting them essentially deobfuscate themselves. My way, it took under 5 minutes, start to finish.
Article Link: https://biebermalware.wordpress.com/2019/04/29/ursniff-maldoc-deobfuscation/