This TSUBAME Report Overflow series discusses observation trends from TSUBAME sensors both in Japan and overseas, as well as other topics not covered in the JPCERT/CC Quarterly Report. This article covers monitoring results from April to June 2026.
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
Note: Starting in FY2026, the JPCERT/CC Internet Threat Monitoring Report has been integrated into the JPCERT/CC Quarterly Report.
Sharp Increase in Mirai-like Packets Targeting 23/TCP Observed in Early May 2026
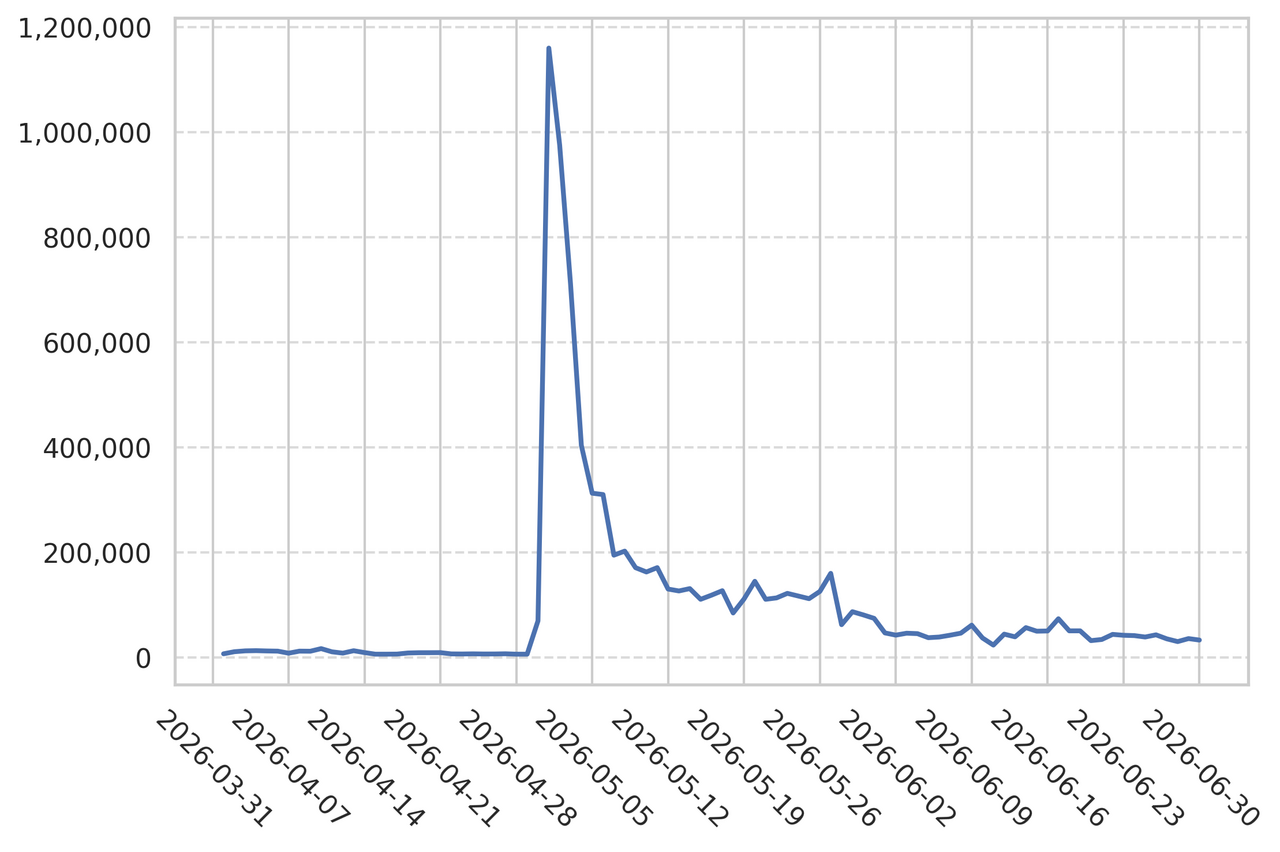
In early May 2026, TSUBAME observed a sharp increase in packets targeting 23/TCP that exhibited Mirai-like characteristics (Figure 1). The number of packets surged on April 30, 2026, before gradually declining.
|
| Figure 1: Trend in the number of Mirai-like packets targeting 23/TCP observed by sensors in Japan |
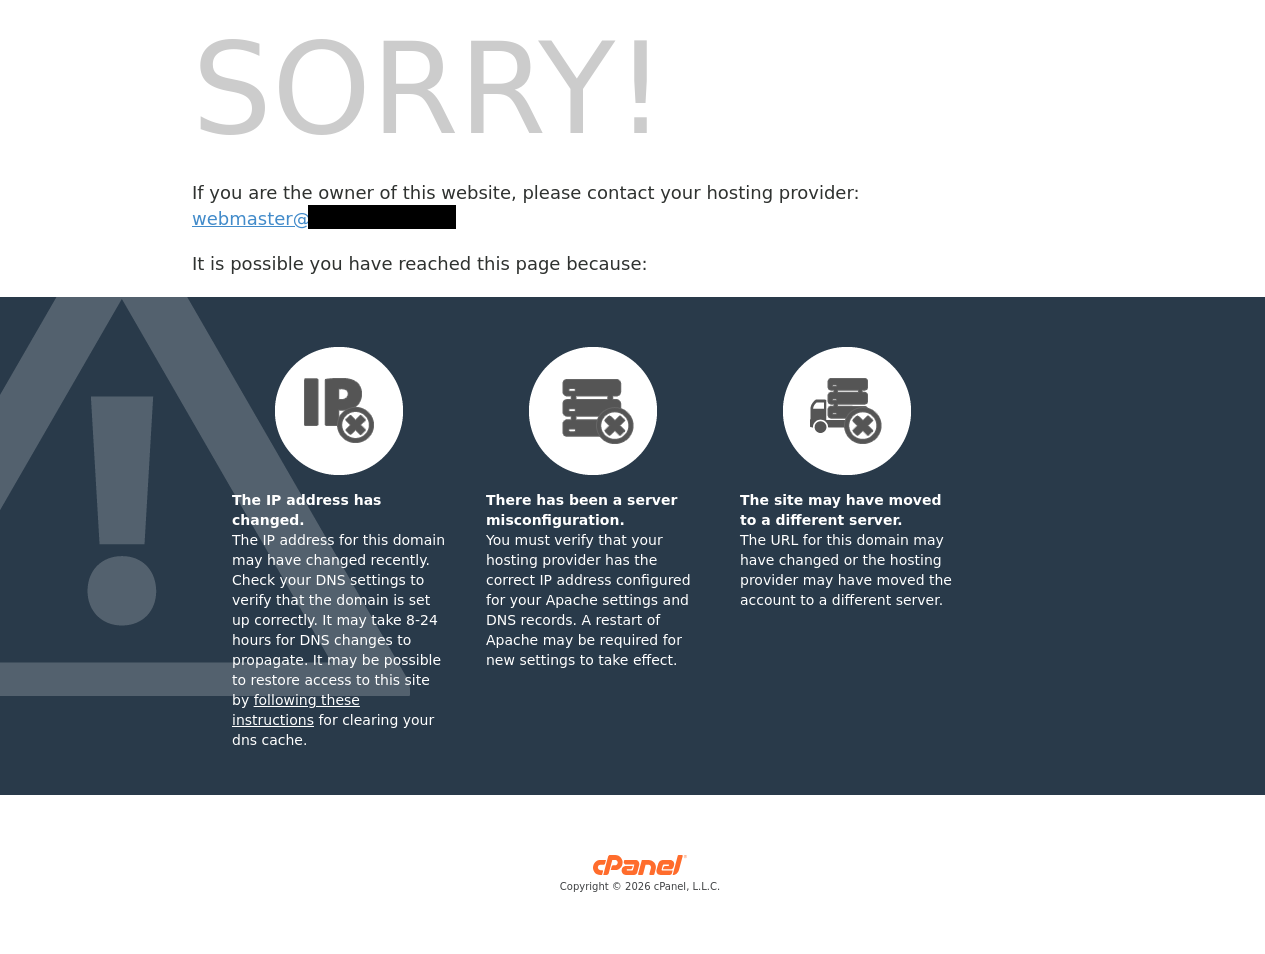
Analysis of the source IP addresses found that many were assigned to several hosting providers. Accessing these IP addresses through a web browser revealed cPanel administration interfaces on many of the hosts (Figure 2).
|
| Figure 2: Example of an interface that appears to be running cPanel |
Although the cause cannot be determined from observation data alone, a Censys blog post [1] and information published by the NICTER Analysis Team [2] during the surge suggest that the increase may have been associated with infection activity involving Mirai or its variants that exploited a vulnerability in cPanel/WHM (CVE-2026-41940). This vulnerability could allow attackers to bypass authentication and compromise affected systems. Other types of damage unrelated to infections involving Mirai or its variants have also been reported.
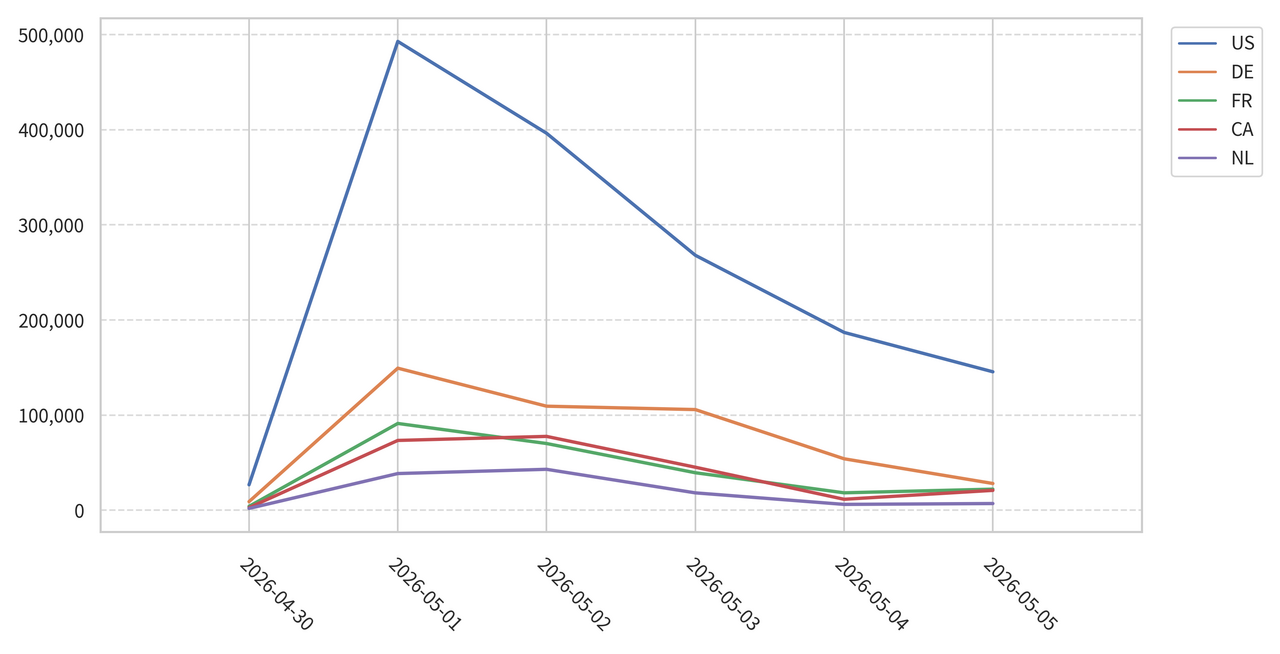
When the packets were aggregated by source region, the United States accounted for the largest share. Sharp increases were also observed around May 1 in several other regions, including Germany, France, and Canada (Figure 3). However, shifts in the regional distribution of the packets suggest that the infections were not concentrated in any particular region, but were spread broadly across the Internet.
|
| Figure 3: Observation trends around May 1, 2026, by major source region |
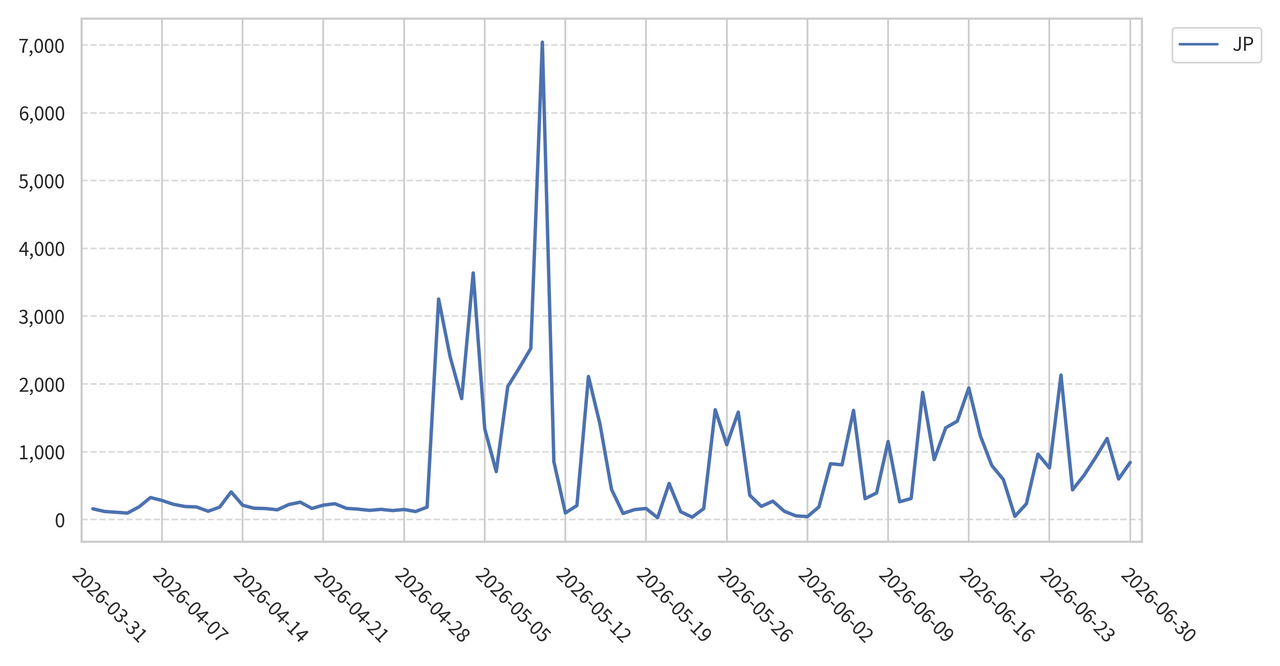
Traffic originating from Japan during the same period showed a similar pattern, increasing to approximately 15 times the level observed before the surge (Figure 4). At the peak, a large number of packets originated from IP addresses assigned to several hosting providers.
|
| Figure 4: Trend in the number of Mirai-like packets originating from Japan and targeting 23/TCP |
Mirai and its variants are generally associated with infections of IoT devices, but infections are not limited to such devices. As this case illustrates, servers can also be compromised. Measures against Mirai and its variants are the same regardless of the type of device and include promptly addressing vulnerabilities, restricting remote access, and replacing weak passwords. If an infection is suspected, review running processes and network communications, paying particular attention to whether the system is operating as intended.
Comparison of the observation trends in Japan and overseas
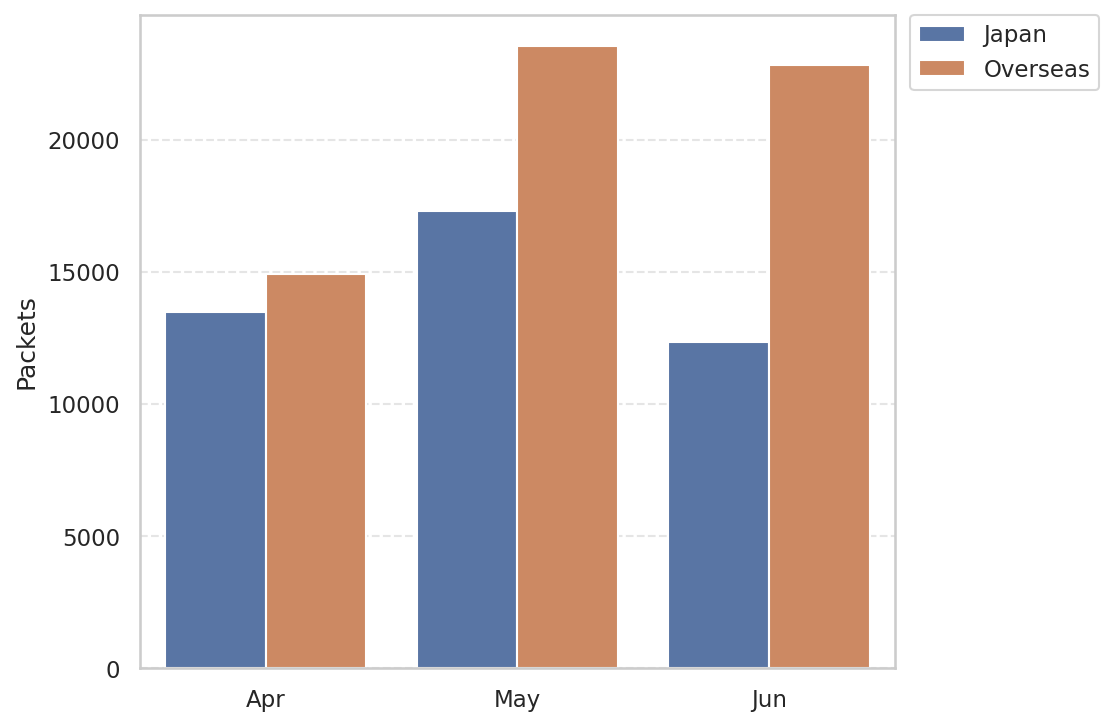
Figure 5 shows a monthly comparison of the average number of packets received by each sensor per day in Japan and overseas. Overseas sensors received more packets than domestic sensors. In May 2026, packet volumes increased across both domestic and overseas sensors, partly due to the sharp increase in Mirai-like packets targeting 23/TCP observed in early May, as described above. In June 2026, the number of packets observed by domestic sensors decreased.
|
| Figure 5: Monthly comparison of the average number of packets received in Japan and overseas |
Comparison of monitoring trends by sensor
Each sensor is assigned a unique global IP address. To examine differences in observation trends among sensors in Japan, North America, Europe, and other regions, Table 1 summarizes the top 10 destination ports observed by each sensor. 23/TCP was the most frequently observed port on most sensors, although some sensors observed more traffic targeting 443/TCP. While the rankings differed among sensors, traffic targeting 80/TCP, 8080/TCP, and 22/TCP was observed by almost all sensors. This suggests that scanning activity targeting these ports is being conducted across a wide range of networks.
Table 1: Comparison of top 10 packets by domestic and overseas sensors
| Japan #1 | Japan #2 | North America #1 | North America #2 | Europe #1 | Europe #2 | Other regions #1 | Other regions #2 | |
|---|---|---|---|---|---|---|---|---|
| #1 | 23/TCP | 23/TCP | 23/TCP | 443/TCP | 23/TCP | 23/TCP | 23/TCP | 23/TCP |
| #2 | 443/TCP | 443/TCP | 443/TCP | 80/TCP | 443/TCP | 443/TCP | 443/TCP | 443/TCP |
| #3 | ICMP | 80/TCP | 80/TCP | ICMP | 80/TCP | ICMP | 80/TCP | 80/TCP |
| #4 | 80/TCP | ICMP | ICMP | 8080/TCP | ICMP | 80/TCP | ICMP | 22/TCP |
| #5 | 22/TCP | 22/TCP | 22/TCP | 22/TCP | 22/TCP | 22/TCP | 8080/TCP | ICMP |
| #6 | 3389/TCP | 3389/TCP | 3389/TCP | 3389/TCP | 8080/TCP | 8080/TCP | 22/TCP | 3389/TCP |
| #7 | 8080/TCP | 8080/TCP | 8080/TCP | 23/TCP | 3389/TCP | 3389/TCP | 3389/TCP | 8080/TCP |
| #8 | 5555/TCP | 5555/TCP | 8443/TCP | 8728/TCP | 8728/TCP | 8728/TCP | 8728/TCP | 8728/TCP |
| #9 | 8443/TCP | 2222/TCP | 8728/TCP | 8443/TCP | 8443/TCP | 8443/TCP | 8443/TCP | 8443/TCP |
| #10 | 2222/TCP | 8443/TCP | 2222/TCP | 2222/TCP | 2222/TCP | 5900/TCP | 2222/TCP | 3000/TCP |
In closing
Monitoring at multiple locations enables us to determine whether certain changes are confined to specific networks. Although no unusual activity warranting an extra issue or special alert was observed this quarter, it remains important to continue monitoring scanning activity closely. We will continue to publish quarterly blog articles in conjunction with the release of the report and provide additional reports when significant changes are observed. We welcome your feedback on this series. Please use the comment form below to let us know which topics you would like us to cover in future articles. Thank you for reading.
Keisuke Shikano
(Translated by Takumi Nakano)
[1] censys, blog "The cPanel Situation Is…", https://censys.com/blog/the-cpanel-situation-is/
[2] NICTER Analysis Team, https://x.com/nicter_jp/status/2052643232685936788
Article Link: TSUBAME Report Overflow (Apr-Jun 2026) - JPCERT/CC Eyes | JPCERT Coordination Center official Blog