July brought another set of threat coverage updates designed to help security teams work faster and with more confidence. ANY.RUN added 42 behavior signatures, 11 YARA rules, and 703 Suricata rules, giving SOCs broader visibility across files, malware behavior, and network activity.
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
We also published new threat intelligence and technical research on active malware and phishing campaigns. Together, these updates help teams validate alerts sooner, reduce manual investigation work, and make faster response decisions.
Here is a closer look at July’s threat coverage and research updates.
Threat Intelligence Report
In July, we published a new Threat Intelligence Report covering ORACLESPY, Rokarolla, and ZOHOMURK.
Available to TI Lookup Premium users, the report includes IOCs, detection guidance, MITRE ATT&CK mappings, and TI Lookup queries for exploring related activity and sandbox sessions.
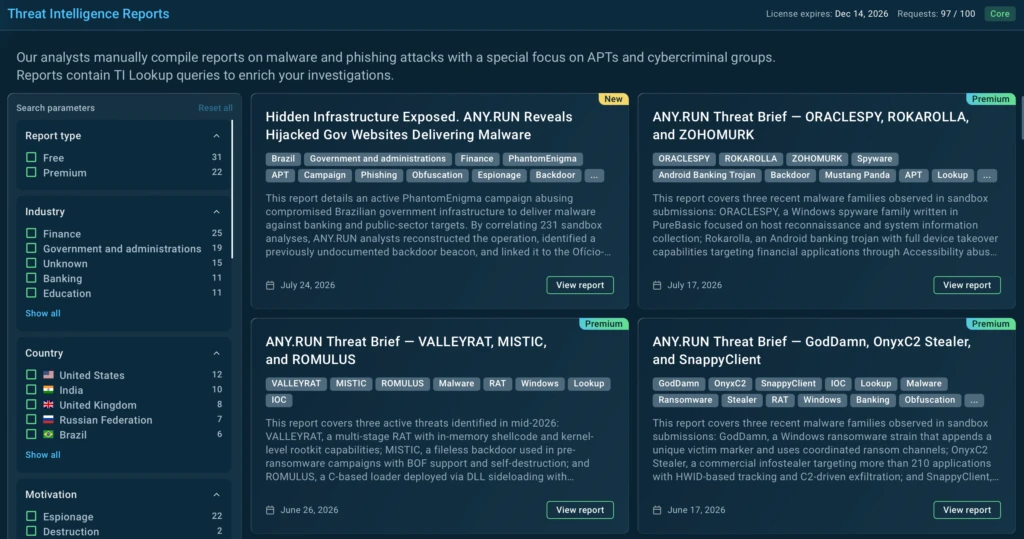 TI Reports on malware and phishing attacks for deeper investigations
The report covers:
- ORACLESPY: Windows spyware that collects system and storage information before preparing it for exfiltration.
- Rokarolla: An Android banking trojan targeting more than 200 banking and cryptocurrency applications through fake apps, overlays, and Accessibility Services abuse.
- ZOHOMURK: A Windows backdoor linked to Mustang Panda that uses Zoho WorkDrive for command-and-control communication and data exfiltration.
Behavior Signatures
In July, we added 42 new behavior signatures to ANY.RUN’s Interactive Sandbox. These updates help security teams identify malicious activity earlier and reduce the time spent manually reviewing processes, files, registry changes, and network connections.
The new coverage includes:
By highlighting family-specific activity directly in sandbox sessions, these signatures help teams validate alerts faster, reduce unnecessary escalations, and move more confidently toward response.
YARA Rules
In July, we added 11 new YARA rules to strengthen static malware detection in ANY.RUN.
Combined with behavior signatures and network detections, the new YARA coverage helps teams build a clearer picture of each threat and make faster investigation decisions.
Turn threat intelligence into faster response decisions.
Give your team the context needed to act sooner.
Suricata Rules
In July, we added 703 new Suricata rules to ANY.RUN’s Interactive Sandbox. These updates help security teams detect malicious network activity earlier and reduce the time spent manually reviewing connections, requests, and command-and-control traffic.
- Kratos related URL chain observed (sid: 84003881): Detects Kratos PhaaS resources fetch HTTP activity
- Hiring and Events-themed phishing URL observed (sid: 89004057): Identifies social engineering threats based on hiring & events invitation lures
- SalatStealer HTTP activity (sid: 84003924): Tracks SalatStealer CnC check-in attempts via HTTP
Latest Threat Research
In July, ANY.RUN researchers published four new investigations into active malware and phishing campaigns. The findings provide practical indicators and detection insights that teams can use to investigate related activity and strengthen their response.
- Kratos PhaaS: An investigation into three generations of the Microsoft 365 phishing kit that uncovered 1,484 previously unattributed sandbox sessions and new fingerprints for threat hunting.
- PhantomEnigma: Research into an active campaign abusing more than 20 compromised Brazilian government websites to deliver malware to banking and public-sector targets.
- Kali365: An analysis of a device code phishing kit that abuses legitimate Microsoft authentication to gain access to Microsoft 365 accounts without directly stealing passwords.
- Banana RAT Evolution: A comparison of two malware branches connected to the same infrastructure, revealing changes in persistence, command-and-control communication, and other behavior.
Strengthen threat detection across your SOC.
Turn suspicious activity into clear investigation evidence.
About ANY.RUN
ANY.RUN is a leading provider of interactive malware analysis and threat intelligence solutions for SOCs, MSSPs, and security teams.
The Interactive Sandbox helps teams safely analyze suspicious files, URLs, and phishing attacks while observing real-time behavior across processes, network connections, files, registry activity, and browser interactions. Threat Intelligence adds further context, helping teams connect findings, investigate related activity, and improve detection coverage.
More than 600,000 security professionals across 15,000 organizations use ANY.RUN to validate alerts faster, reduce manual investigation work, and respond to threats with greater confidence.
The post Threat Coverage Digest: New TI Report, Threat Research and 750+ Detection Rules appeared first on ANY.RUN's Cybersecurity Blog.
Article Link: July Threat Coverage Digest: TI Report and 750+ Detection Updates