Supermarket freezer attacks have moved beyond France. Overnight into Monday, November 2, 2026, refrigeration systems at dozens of stores in Belgium, Luxembourg and Sweden showed sudden temperature rises, with some freezers set as high as 50°C. Retailers threw out spoiled stock, and several stores opened late or stayed closed for the morning.
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
The incidents are suspected cyberattacks. Sweden’s national cybersecurity center says it is responding to multiple incidents involving store cooling systems, and the refrigeration contractor that runs Delhaize’s installations in Belgium has called the Belgian events a cyberattack. As of November 2, no group has claimed responsibility, and no authority has named a suspect or an entry point.
Which Retailers Reported Problems?
Reports from retailers, local media and wire services put the scope as follows. Store counts vary between outlets, so the table gives the range where they differ.
| Country | Retailer | Reported Impact |
|---|---|---|
| Belgium and Luxembourg | Delhaize (Ahold Delhaize) | About 40 stores; the company describes an “IT incident” affecting fridges and freezers |
| Belgium | Carrefour Belgium | 15 stores; all remained open |
| Belgium | Spar stores operated under Colruyt Group franchise | Five shops; smaller Proxy Delhaize and Shop & Go outlets were also reported |
| Sweden | ICA | “A limited number” of stores operating outside ICA’s central network |
| Sweden | Coop | Six or seven of roughly 800 stores; Coop says the situation is contained |
| Estonia | Unnamed grocery chain | Temperatures set to 50°C, as reported by its refrigeration technology supplier |
Store-level losses are already significant. One Delhaize store in Hoeilaart, Flemish Brabant, put its lost produce at €100,000, not counting revenue lost while closed. A Stockholm ICA store said the attack hit at 2 a.m. and staff noticed it at 5:30 a.m., and stores in Sjöbo and Tomelilla in southern Sweden stayed shut for the morning.
What Happened Inside the Cooling Systems?
The clearest technical account so far comes from Belgium. Stephan Moelans, CEO of refrigeration contractor Sabcobel, which operates Delhaize’s installations, told Belgian news agency Belga that the units’ evaporators had been switched into defrost mode. He said Sabcobel started sending technicians at 1 a.m. and spent the night and morning disconnecting the affected installations.
In Sweden, one ICA store posted that its fridge and freezer temperatures had been “hacked” overnight and set to 50°C. Another store wrote that the settings matched those seen during the French attack.
Neither retailers nor authorities have named the controller brands involved in these incidents. That matters: in France, more than one vendor’s equipment was targeted, so it is not safe to assume the same product line was hit in Belgium or Sweden.
Is This Confirmed as a Cyberattack?
Not formally. The evidence so far points toward remote tampering, but the wording from each party differs:
- Sweden’s national cybersecurity center: Head John Billow confirmed the center is working on several incidents affecting grocery refrigeration and said Sweden has “quite a lot of exposed operational technology devices” that need updating or patching
- Belgian refrigeration contractor: Sabcobel’s CEO described the Belgian events as a cyberattack
- Ahold Delhaize: Calls it an IT incident under investigation
- ICA and Coop: Confirm overnight incidents affecting refrigeration and freezer systems at a limited number of stores
- Belgian and Swedish national cyber agencies: Both say they are monitoring the incidents
Ahold Delhaize separately dealt with an October security issue that forced it to shut down and later restore some IT systems, and it reported suspicious activity to Dutch police last month. No source has linked that earlier incident to the refrigeration problems.
The Same Overnight Pattern, Three Times in Three Months
The November incidents look like the French supermarket cyberattack of October 11 to 12, and both resemble refrigeration failures at U.S. military commissaries in August. A shared attacker has not been established for any of them.
The table below compares the three waves in detail, including the equipment named so far, which has been disclosed only for France.
U.S. Military Commissaries
Late August 2026
- Scale
- At least six commissaries
- Observed effect
- Freezers entered defrost mode overnight
- Equipment named
- Not disclosed
- Status
- Suspected cyberattack
Joint DCIS-led investigation
France
Night of October 11 to 12, 2026
- Scale
- Up to about 700 supermarkets, per the French government
- Observed effect
- Forced defrost cycles and temperatures around 50°C; food losses and fires
- Equipment named
- Danfoss AK-SM and AK-SC, Copeland xweb and Dixell xweb controllers
- Status
- Confirmed compromises
Paris prosecutor investigating
Belgium, Luxembourg, Sweden
Night of November 1 to 2, 2026
- Scale
- Dozens of stores
- Observed effect
- Defrost mode and setpoints of 50°C
- Equipment named
- Not disclosed
- Status
- Suspected
National agencies responding
No shared attacker has been established across the three waves. Status as of November 2, 2026.
The U.S. Army’s Criminal Investigation Division has said it is working with French law enforcement to understand the European outages. That coordination does not show the incidents share an attacker. Separate open-source analysis has also traced the unclaimed pattern from the commissaries to France.
Why Refrigeration Controllers Keep Getting Hit
Large stores run their refrigeration through centralized controllers that manage setpoints, alarms and defrost schedules for every case and cold room. Maintenance firms often reach these controllers remotely, and some sit directly on the internet with a web management interface.
France’s CERT-FR alert on the October attack warned that exposing these interfaces goes against basic practice and that the campaign was probably still ongoing. It said an end-of-life controller left online has a very high chance of compromise, and that a factory reset alone does not help, because the device stays vulnerable and is likely to be hit again. SOCRadar’s own October snapshot found roughly 2,900 exposed Danfoss StoreView services in France alone.
The risk is not limited to one country. Swedish officials now say they have many exposed operational technology (OT) devices to fix, and retailers often depend on contractors who control the remote access path.
Who Could Be Behind It?
No group has claimed the French, U.S. or new European incidents, and no government has attributed them. The attacks so far show no ransom demand or data theft, which makes disruption the more likely goal than profit.
Commentators have raised state-backed sabotage as one explanation, while others note that unsecured controllers are within reach of low-skilled actors. Both readings remain possible. Until there is a credible claim or official attribution, any link to a named group should be treated as speculation.
What Retailers and Refrigeration Contractors Should Check Now
CERT-FR’s guidance from the French incident applies to any retailer running remotely managed refrigeration, whatever the vendor:
- Remove refrigeration controllers from direct internet exposure, including any unit on a public IP address
- Restore remote access only through a secured VPN or protected network; filtering contractor source IPs is an emergency measure, not a fix
- Review the full controller configuration, especially defrost schedules, temperature setpoints and alarm settings
- If a controller shows signs of tampering, restart or factory reset it and reconfigure it before reconnecting, but only after the exposure is closed
- Update firmware, apply the vendor’s strictest security mode where one exists and confirm default passwords are changed
- Plan replacement of end-of-life controllers that no longer receive updates
Retailers should also ask their refrigeration contractors how they connect to each store and who holds those credentials. Independent temperature alarms that do not depend on the controller give staff a second warning at night, when every one of these incidents began.
Protect Your OT Systems and Supply Chain with SOCRadar
In every country hit so far, the attacks targeted refrigeration controllers managed remotely by contractors. CERT-FR found the compromised French controllers exposed to the internet, and Sweden’s cybersecurity center reports many exposed OT devices still waiting for updates. Security teams rarely see these systems. SOCRadar helps close that gap in three ways:
- Attack Surface Management: Finds refrigeration management interfaces and remote access services exposed across your IP space, including ones a contractor set up without your security team’s knowledge, so you can take them offline before attackers find them
- Supply Chain Intelligence: Tracks the security posture of refrigeration contractors and other OT service providers, and flags when a supplier you depend on shows signs of compromise
- Dark Web Monitoring: Watches hacktivist channels and underground forums for attack claims, leaked access or chatter that names your brand, your suppliers or the food retail sector
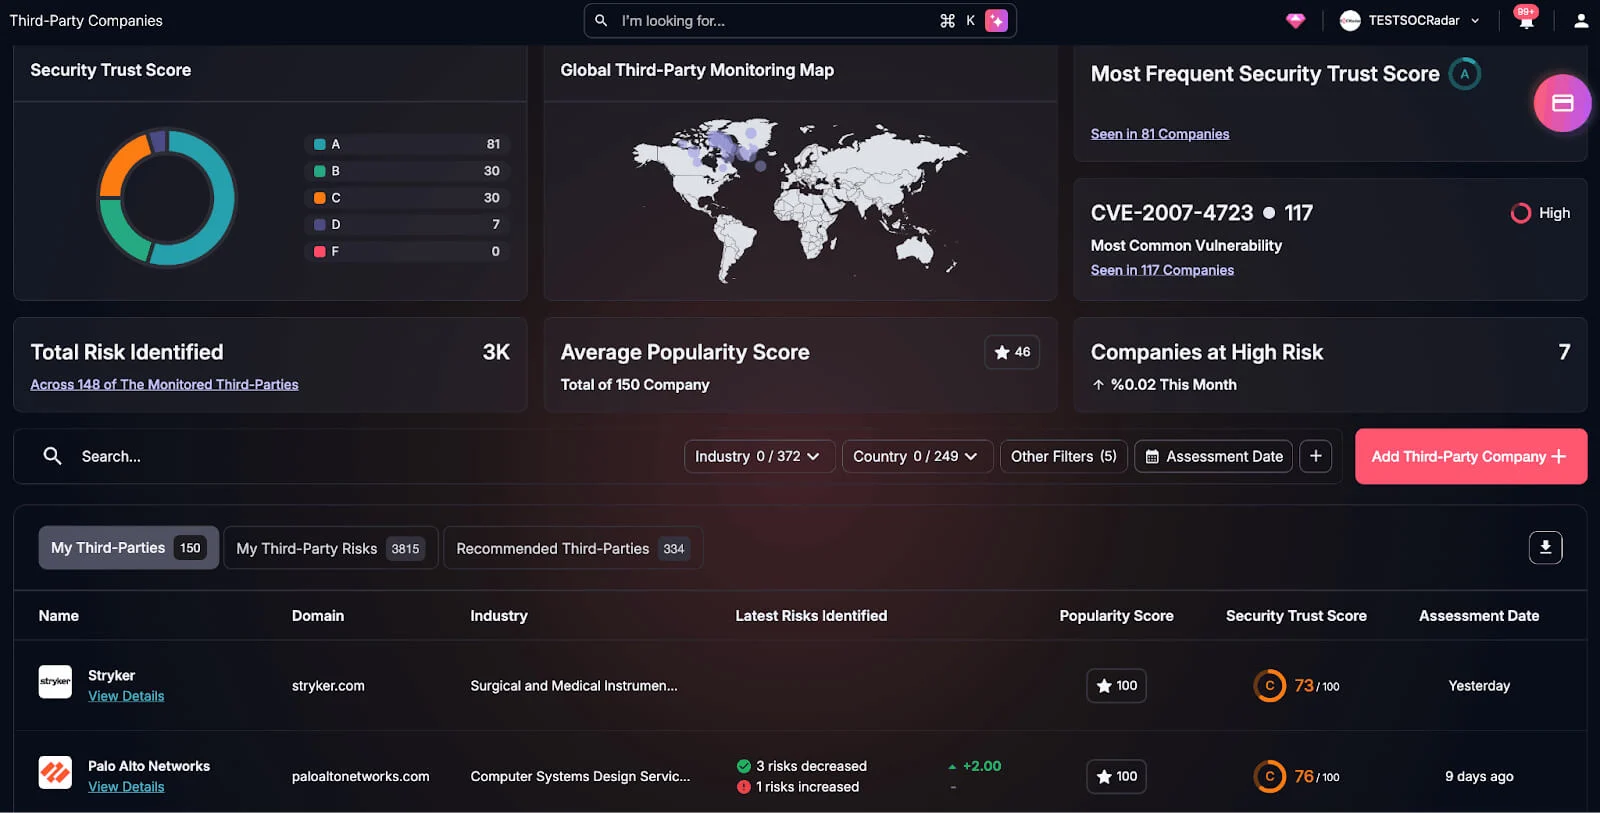 Third-party companies, SOCRadar Supply Chain Intelligence module
External visibility shows where you are exposed and who is talking about you, but only a controller’s own configuration and event logs can confirm whether it was changed. Every one of these incidents happened overnight, when no one was watching the cases. Taking exposed controllers off the internet and reviewing contractor access now is the best preparation for the next wave.
Article Link: https://socradar.io/blog/supermarket-freezer-attack-belgium-sweden-luxembourg/