GangExposed, the anonymous leaker who spent 2025 exposing Conti and Trickbot leadership, has moved on to Qilin. A new post on the channel shares an investigation naming a Russian national as “Haise”, the persona that has fronted Qilin’s affiliate program on underground forums since 2022.
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
The timing is hard to ignore. Only weeks ago, Germany arrested a Russian national suspected of being a leading Qilin member after extradition from Japan. Nothing public connects that suspect to Haise, and no authority has confirmed GangExposed’s identification.
What we have is a single investigator’s chain of forum records, Telegram history and leaked Russian databases, and it deserves a careful read before anyone treats the name as settled.
 Photos of the individual GangExposed names as Haise, as published in the investigation; blurred and redacted by SOCRadar
Key Takeaways
- GangExposed published an investigation naming a Russian national as Haise, Qilin’s long-standing administrator persona.
<li>
  The identification rests on forum profiles, Telegram history and leaked Russian databases, and <strong>has not been independently verified</strong>.
</li>

<li>
  <strong>Haise’s role in Qilin</strong> is well documented, dating back to the persona’s arrival on RAMP in May 2022.
</li>

<li>
  <strong>No public source links Haise</strong> to the suspected leading Qilin member arrested in Germany in October 2026.
</li>

<li>
  Qilin keeps operating, with <strong>more than 2,350 known victims across 62 countries</strong>.
</li>
Haise Before the Leak
Haise is one of the better-documented personas in the RaaS ecosystem. The profile joined the Russian-language RAMP forum on May 29, 2022, shortly before the group surfaced as Agenda, and was openly advertising Qilin’s affiliate program by February 13, 2023.
Over the following years, Haise has been the voice of the program. In March 2023, researchers who infiltrated Qilin reached the persona over Tox and learned that affiliates kept 80% of ransom payments up to $3 million and 85% above that.
In July 2023, Haise explained on RAMP that ransoms land in affiliates’ wallets first, with the operators’ share forwarded afterward. In June 2025 came the “call lawyer” feature, pitched to affiliates as legal support for squeezing victims during negotiations. A month later, a Telegram channel impersonating Europol offered rewards for Haise and a second administrator persona, “XORacle”. Europol called it a scam.
So the public role is not in question. The identity behind it is what GangExposed claims to have solved.
How the Identification Was Built
The write-up describes “a chain of data linking the alias Haise to a specific individual” that “runs in one direction and is corroborated in reverse”, and closes with “a high degree of confidence” in the result.
We are not reproducing the personal data in the investigation, but its logic can be summarized. It starts with RAMP approval logs from June 2022 that list “haise” among new members, and matches the persona to profiles on Exploit and XSS.
A shared second alias across those profiles, plus a Telegram handle and an email address listed on them, carries the trail to other forums, including a dump of roughly 25,000 accounts from a third forum. From there the investigation moves into leaked Russian data: the email appears in a public services database that points to a named individual, and a relative’s leaked records lead to a phone number tied to a Telegram account, cross-checked against a leaked mobile subscriber database.
That Telegram account is where the story gets more texture. It was active in public groups from September 15, 2018, to July 29, 2024, and has since been deleted. The messages read like someone running ransomware operations rather than dabbling: recruiting penetration testers for Windows, Linux, ARM, NAS and ESXi in April 2023, asking for forums with pentesters “apart from Exploit, XSS, and RAMP”, digging into how the ESXi kernel works, asking how to bypass and disable a major EDR product in August 2023, and asking “Who works with corporate targets?”
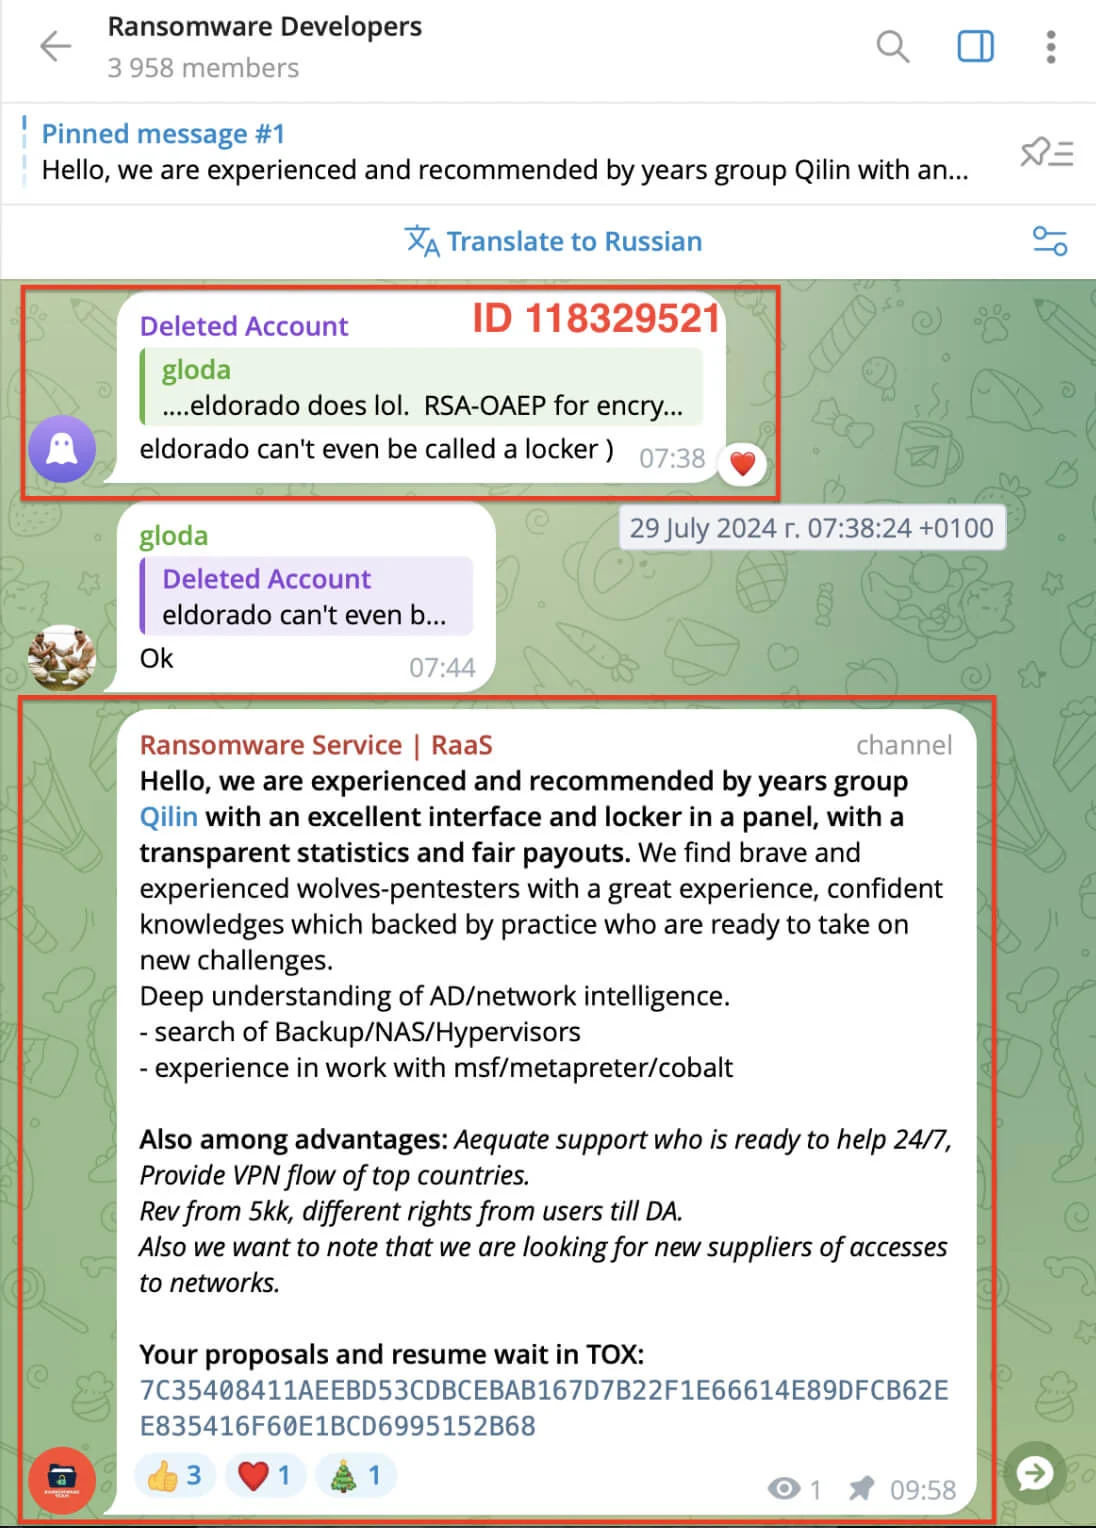 Qilin advertisements and surrounding Telegram group messages cited in the investigation
The write-up also points to Qilin ads posted in the same groups on July 22, July 29 and August 7, 2024, and says the Qilin brand appears nowhere else in those groups. On July 29, 2024, the account replied within seconds to a group post about reporting that Scattered Spider had added Qilin and RansomHub to its toolkit.
How Much Weight It Carries
Our view is that the chain is plausible and worth tracking, but it is not proof. Several links depend on leaked Russian government, telecom and forum data whose integrity cannot be checked from the publication. The first and most important step, from Haise to the Exploit and XSS profiles, appears to rest on the order of names in approval records rather than a shared unique identifier.
The Telegram messages fit a ransomware operator, yet interest in ESXi and EDR evasion describes a lot of people in those groups, not only an administrator. There is also a small internal inconsistency: the narrative places a Qilin ad “one week” after the July 29, 2024, post, while its own ad dates start on July 22.
GangExposed’s track record cuts both ways. When the channel named Conti and Trickbot leader “Stern” in 2025, German police later confirmed the identity. The same reporting notes that some researchers see the leaker as a former insider settling scores or recycling older material. Either way, the channel has shown sustained access to Russian-speaking ransomware circles, and the Qilin post widens its campaign beyond the Conti ecosystem.
Where Qilin Stands Now
Qilin started as Agenda in July 2022, rebranded that September, and builds payloads for Windows and VMware ESXi in Rust and Go. It became one of the defining RaaS brands of 2025, adding more than 185 victims to its leak site in October 2025 alone, including claimed attacks on Asahi, US local governments and Texas power companies, per reporting at the time. Its tally now stands at more than 2,350 known organizations across 62 countries, with more than 450 victims listed since June 2026.
The pressure is building, though. Threat group tracking shows Qilin lost the leak site volume lead to The Gentlemen in June 2026 and saw volume halve after its Q3 2026 peak, while continuing to operate after the October arrest. A public identification of its administrator adds another layer of risk for the people behind the brand, and for affiliates weighing whether to stay.
Bottom Line
GangExposed has put a name to one of the most visible personas in the RaaS economy, and the case it lays out is detailed enough to take seriously. It is also built almost entirely on leaked data and one investigator’s linkage, with no confirmation from the authorities who already have a Qilin suspect in custody. We treat the identification as a credible lead that still needs confirmation.
For Qilin itself, the exposure lands at a bad moment: declining leak site volume, a suspected core member under arrest and now its public face allegedly unmasked. The more useful signal over the coming weeks will be whether its affiliates stay or move to other programs.
FAQ
Who Is Haise in the Qilin Ransomware Group?
Haise is the RAMP forum persona widely described as Qilin’s administrator. The profile joined RAMP in May 2022, advertised Qilin’s affiliate program in February 2023 and later announced new panel features such as a “call lawyer” negotiation option. Researchers also used the persona to learn Qilin’s affiliate payout structure in 2023.
Has Haise Been Officially Identified?
No. GangExposed published an investigation naming a Russian national as Haise, but no law enforcement agency has confirmed the identification. The claim relies on leaked databases and forum records that have not been independently verified.
Is the Qilin Member Arrested in Germany the Same Person as Haise?
There is no public evidence of that. Germany arrested a Russian national suspected of being a leading Qilin member in October 2026 after extradition from Japan, but available reporting does not give the suspect’s alias or link them to Haise.
Who Is GangExposed?
GangExposed is an anonymous persona that began publishing internal Conti and Trickbot files on Telegram in May 2025 and named several alleged senior members. One of its identifications, of Conti and Trickbot leader “Stern”, was later confirmed by German police.
Is Qilin Ransomware Still Active?
Yes. Qilin has continued operating after the October 2026 arrest and has listed more than 450 victims on its leak site since June 2026, although its volume has fallen from its 2026 peak.
Does Exposing a Ransomware Administrator Stop Attacks?
Usually not immediately. Affiliates retain their access and tools, and RaaS programs can continue or rebrand. Organizations should keep securing remote access, hardening hypervisors and monitoring for credential leaks regardless of attribution news.
What Should Defenders Do About Qilin Right Now?
The identification does not remove affiliates’ access or tooling, so the practical picture has not changed. In many cases, Qilin affiliates have used stolen administrative credentials found on the Dark Web to get into VPNs (T1078, T1133), and the group’s ESXi payloads make hypervisors a priority target. Enforcing MFA on remote access, rotating leaked credentials and hardening ESXi management remain the most effective steps.
Article Link: https://socradar.io/blog/qilin-ransomware-admin-haise-unmasked/