Vulnerability overview
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
On October 20, 2026, the PHP security team published a preliminary notice regarding an upcoming emergency release that addresses two critical vulnerabilities (both rated 9.2 on the CVSS scale). The patches were released on Wednesday, October 21, 2026, at 14:00 UTC.
The release was expedited after information about the vulnerabilities was leaked to the public before the scheduled embargo was lifted. In a post on Hacker News, a user reported two RCE vulnerabilities in PHP, allegedly affecting all versions starting with PHP 5.4.0.
The vulnerabilities in question are CVE-2026-109618 and CVE-2026-109619. Shortly after the post appeared, researchers confirmed the existence of the vulnerabilities. Along with the leak of details, an exploit unofficially named PHP2Shell appeared online. In the leaked demo video, the exploit is shown in action on web servers running WordPress, MediaWiki, phpBB, Magento, Joomla, Laravel, Symfony, Drupal, and WHMCS — platforms that power many modern websites. The authenticity of the demonstration and the exact behavior of the exploit had not been independently verified at the time of publication.
According to the researcher who published the PoC, the vulnerabilities are related to the handling of the multipart/form-data MIME type in conjunction with the session upload progress mechanism (session.upload_progress) in the PHP core and fall under the categories of use-after-free and memory corruption. This means that the flaws cannot be patched via application code, and the only possible fix is to update PHP on the server. The attack works without authentication: an attacker with network access to a PHP application can execute arbitrary code on behalf of the PHP process without needing to authenticate. Security advisories issued by PHP on October 21 confirm this information.
The vulnerabilities affect PHP versions 5, 6, 7, and 8. As of this publication, branches from 8.2 to 8.5 are supported. Older branches, including PHP 8.1, 8.0, 7.x, and 5.x, have reached the end of their lifecycle; however, due to the critical severity of the vulnerabilities, backported patches have also been released for versions 7.4, 8.0, and 8.1.
Sansec experts estimate that widespread exploitation could begin within 15 minutes of the update’s release. We strongly recommend that administrators responsible for publicly accessible PHP web servers take the following steps before the patch is available:
- Conduct an inventory of all PHP-based systems in the infrastructure (including web servers, control panels, third-party software, etc.).
- Disable upload-progress: set
session.upload_progress.enabled = Offusing thephp_admin_flagin PHP-FPM pools. - Block multipart requests on nginx and Apache servers.
- Consider temporarily isolating PHP applications that connect to the Internet until fixes are released.
- Ensure readiness to install the patch immediately upon its release.
- Plan to migrate servers running unsupported versions (8.1 and earlier) to the latest PHP branch.
Detection by Kaspersky solutions
Kaspersky solutions detect the described malicious activity at various stages of the attack. Possible detection scenarios are listed below.
When an attempt is made to exploit these RCE vulnerabilities, Kaspersky Endpoint Detection and Response promptly alerts the user to suspicious actions performed in the context of a web server, on both Linux and Windows machines. This activity is detected by the following rules:
- creating_windows_shell_from_a_web_servers_process;
- possible_web_shell_creating_via_exploit;
- spawning_process_from_webserver_more_filters_linux;
- webserver_interpreter_execution_linux;
- executable_file_in_www_folder.
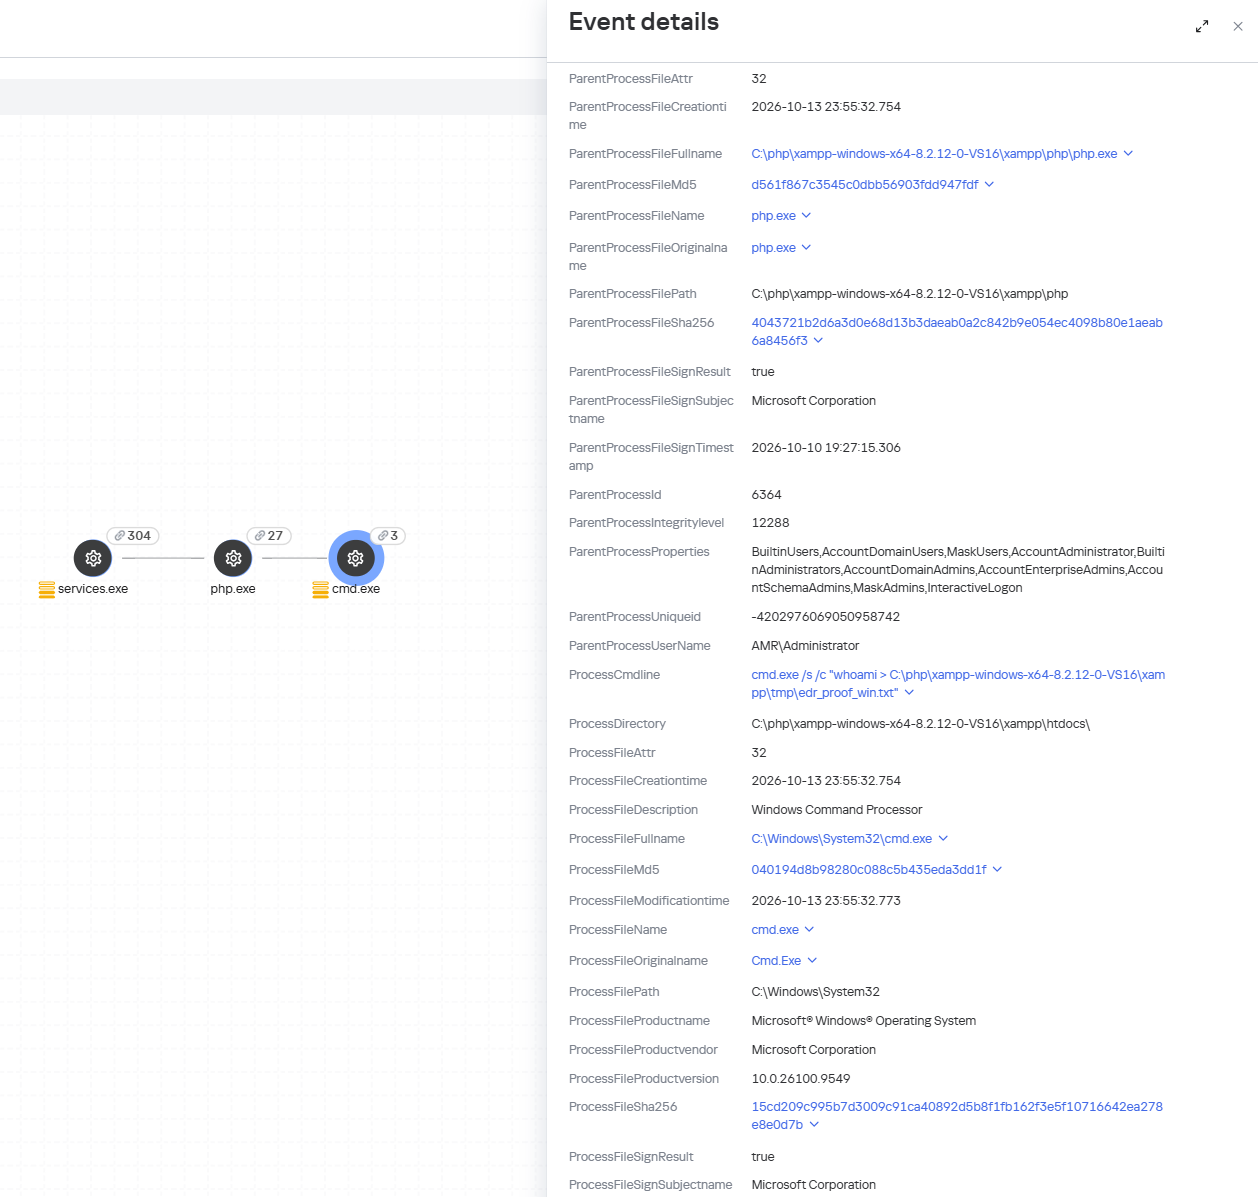
Detection of the PHP2Shell vulnerability exploit by KEDR
Exploitation of the PHP2Shell vulnerability in network traffic is detected by Kaspersky Anti Targeted Attack (KATA). This solution detects such activity with the following verdicts: Exploit.CVE-2026-109618.HTTP.C&C and Exploit.CVE-2026-109619.HTTP.C&C.
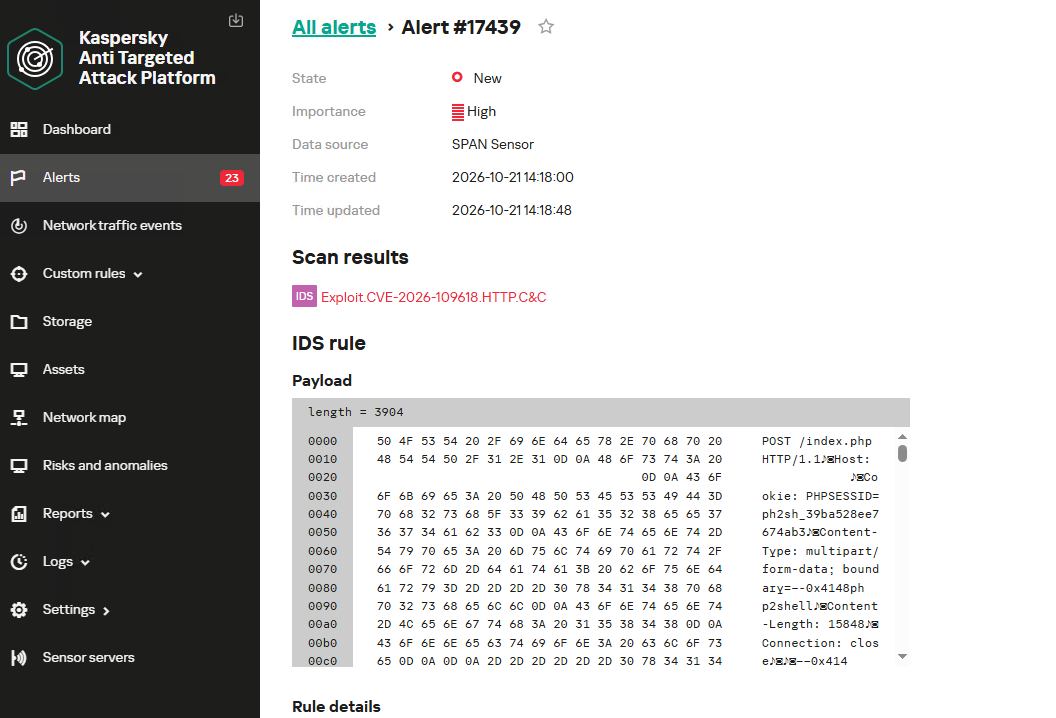
Detection of the PHP2Shell vulnerability exploit by KATA
Our Kaspersky Endpoint Security solution, now available as Kaspersky Next, also detects malicious post-exploitation activity using the Behavior Detection component, such as PDM:Exploit.Linux.Generic and PDM:Exploit.Win32.Generic.
Article Link: https://securelist.com/tr/php2shell-critical-vulnerabilities-in-php/121596/