October marks Cybersecurity Awareness Month, a timely opportunity to look at how American organizations can strengthen their security operations.
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
Among the biggest challenges SOC teams face is making sure they not only detect and investigate threats, but doing so quickly enough to make the right security decisions without overwhelming analysts or increasing operational costs.
In this article, ANY.RUN explores how better threat visibility and automation can help US-based SOCs achieve this, using a real phishing investigation and metrics to demonstrate how faster triage translates into greater ROI from existing SOC investments
Key Takeaways
- Faster triage reduces investigation costs. A healthcare MSSP achieved 76% faster phishing triage with ANY.RUN, reducing investigation time from 30–40 to 4–7 minutes.
- Better visibility supports faster decisions. Behavioral analysis and automation help analysts identify genuine threats without lengthy manual checks.
- More cases resolved at Tier 1 improve SOC capacity. In the same customer case, the Tier 1 closure rate increased from 20% to 70%.
- Higher SOC ROI starts with existing resources. Fewer unnecessary escalations, faster investigations, and better resource utilization help teams scale efficiently.
The SOC Efficiency Challenge: What the Numbers Reveal
SOC teams face a difficult balancing act: alert volumes keep growing, but the time and resources available to investigate them remain limited. Analysts must sort through potentially harmless activity while ensuring that genuine threats don’t go unnoticed.
Recent Microsoft research highlights the scale of the problem:
According to a 2026 Microsoft and Omdia study, 42% of security alerts go uninvestigated, while 46% of respondents believe that more than half of their alerts are false positives.
This means SOC teams spend valuable time filtering out false alarms while a significant share of alerts never receive proper investigation, potentially leaving real threats undetected.
The consequences go beyond analyst fatigue. A total of 91% of surveyed security leaders reported serious security incidents caused by operational gaps.
For US-based organizations, this highlights a critical priority: reduce the time spent on false positives and routine checks to improve efficiency and get greater value from your security investments.
How Visibility and Automation Helps SOCs Increase ROI
Increasing SOC ROI starts with helping analysts make accurate decisions faster, without adding unnecessary manual work or operational costs.
It takes providing analysts with enough information to make accurate decisions for them to avoid spending unnecessary time on manual checks and switching between security solutions.
According to ANY.RUN data, two capabilities have proved to make most difference: visibility into actual threat behavior and automation of repetitive investigation steps. That’s what helps Tier 1 and Tier 2 analysts distinguish genuine threats from false positives, prioritize incidents, and decide when further investigation or response is needed:
- Identify threats faster. Interactive Sandbox reveals actual file and URL behavior, from phishing chains to malware activity, with a median threat detection time of just 14 seconds.
- Reduce manual investigation. Automated Interactivity, integrations, and API access streamline repetitive steps, helping analysts move from alert to decision faster.
- Turn findings into action. Ready-made reports and AI recommendations support informed response decisions, helping reduce unnecessary Tier 1-to-Tier 2 escalations by up to 30%.
- Detect known threats earlier. Around 30% of unique malicious IOCs in studied Sandbox sessions were already present in Threat Intelligence Feeds before investigation, allowing teams to identify some threats without separate Sandbox analysis.
These numbers are achieved through accessible, automated behavioral analysis of URL and file submissions offered by ANY.RUN.
Reach out to us about speeding up triage in your SOC or MSSP.
Our experts will help you optimize your workflows.
It gives analysts the evidence they need to assess alerts and make informed response decisions. Instead of relying on static indicators or reputation scores alone, SOC teams can see what a suspicious file or URL actually does, identify malicious activity, and move from alert to verdict with fewer manual steps.
Use Case: Phishing Investigation, Done Right
In a typical phishing investigation, an analyst may need to manually extract suspicious URLs, follow redirects, and navigate CAPTCHAs before reaching the actual threat.
This real phishing investigation in ANY.RUN shows how this process can be streamlined.
The email contains a QR code leading to a credential-harvesting page disguised as Microsoft 365. Instead of manually navigating the phishing chain, the analyst can rely on Automated Interactivity to extract the URL, follow redirects, and complete the CAPTCHA to reveal the phishing page.
Meanwhile, Interactive Sandbox automatically captures the attack behavior, network activity, and related IOCs, organizing the evidence across the process tree and other analysis tabs.
Even with a multi-step phishing chain like this, Tier 1 can get an initial verdict within seconds. Across ANY.RUN analyses, the average mean time to detect (MTTD) is just 14 seconds.
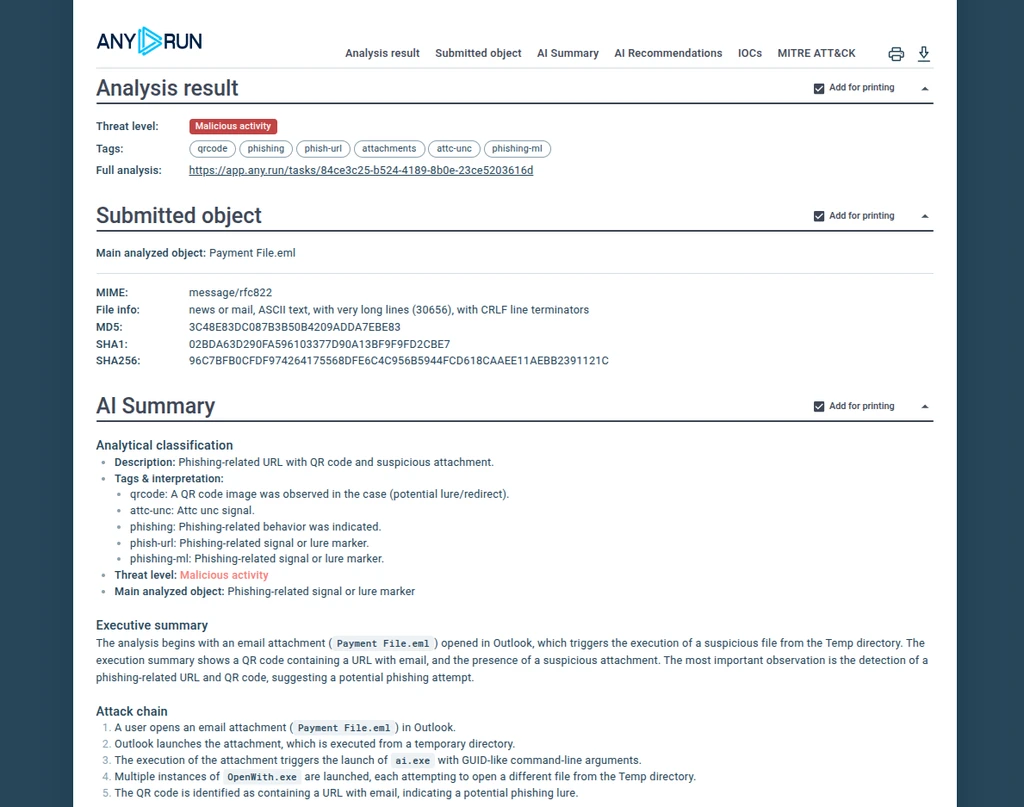 AI-powered Tier 1 reports deliver actionable insights for SOC teams
Once the analysis is complete, the analyst can generate a Tier 1 report containing the verdict, AI-generated summary, and recommended next steps. In this scenario, these recommendations can help the team look for similar phishing emails, identify users who may have opened the page, and investigate potential credential exposure.
This workflow can be further accelerated using ANY.RUN’s selection of ready-made integrations as well as API/SDK capabilities. As noted by one of ANY.RUN’s MSSP clients, this setup significantly contributes to triage speed:
“The integration worked much better than was expected. With minimal changes in the workflow, we achieved stronger results: Tier 1 analysts had far more capacity; analysis of both low- and high-priority incidents became
Threat Intelligence adds another layer of context. Threat Intelligence Lookup helps determine whether the extracted indicators have appeared in other investigations and what behavior they were associated with. Meanwhile, Threat Intelligence Feeds deliver verified malicious IOCs into existing security workflows, supporting earlier detection of related threats.
The key outcome isn’t simply a completed analysis, but a faster, evidence-based decision.
With a confirmed verdict, enriched threat data, and a structured report, Tier 1 can determine whether to close the alert or escalate the incident. If further response is needed, the next team receives the relevant findings without having to repeat the investigation.
This approach helps SOC teams resolve more cases at Tier 1 and reserve specialist time for complex threats. Across customer workflows, ANY.RUN helps reduce Tier 1-to-Tier 2 escalations by up to 30%, improving response efficiency without increasing analyst workload.
76% Faster Triage: Measuring the Impact on SOC Operations
The phishing example shows how individual investigations can become faster and more efficient. But here’s what happens when these improvements are applied across an entire SOC:
<thead> <tr>
<th>
For SOC Analysts </th>
<th>
For SOC Leaders </th>
</tr>
</thead><tbody> <tr>
<td>
<div><p>76% faster phishing triage: Investigation time reduced from 30–40 to 4–7 minutes</p></div> </td>
<td>
<div><p>Tier 1 closure rate increased from 20% to 70%: More alerts resolved without escalation</p></div> </td>
</tr>
<tr>
<td>
<div><p>14-second threat detection: Faster verdicts and prioritization</p></div> </td>
<td>
<div><p>21-minute reduction in MTTR per incident: Faster resolution contributes to lower operational costs</p></div> </td>
</tr>
<tr>
<td>
<div><p>Less manual investigation: More alerts reviewed per analyst</p></div> </td>
<td>
<div><p>Greater SOC capacity: More cases handled without proportional headcount growth</p></div> </td>
</tr>
<tr>
<td>
<div><p>Clearer evidence and handoffs: Fewer unnecessary escalations</p></div> </td>
<td>
<div><p>Better resource allocation: Tier 2 specialists focus on complex incidents</p></div> </td>
</tr>
<tr>
<td>
<div>Faster alert-to-decision time: More consistent investigation workflows.</div> </td>
<td>
<div><p>Improved SLA adherence: More predictable response times and service quality</p></div> </td>
</tr>
</tbody></table>
Turning Faster Triage Into Higher SOC ROI
For US-based SOCs, increasing ROI doesn’t necessarily mean investing in more security solutions or expanding headcount. It starts with getting more value from existing resources.
By combining behavioral visibility, automation, and actionable threat intelligence, SOC teams can investigate more alerts, resolve more cases at Tier 1, and reduce the time spent on manual work and unnecessary escalations.
Reduce Tier 1-to-Tier 2 escalations by up to 30%.
Streamline SOC operations for a higher ROI.
As the 76% faster triage example demonstrates, these operational improvements can translate into greater analyst capacity, lower investigation costs, and stronger returns on SOC investments.
About ANY.RUN
ANY.RUN provides interactive malware analysis and actionable threat intelligence for SOC teams and MSSPs. Its Interactive Sandbox, TI Lookup, and TI Feeds help organizations detect threats faster, automate investigations, and make informed response decisions.
Trusted by 16,000+ organizations worldwide and 74 of Fortune 100 companies, ANY.RUN helps security teams improve operational efficiency and maximize the value of their security investments.
FAQ
Alert overload, false positives, and limited analyst capacity are major challenges. According to a 2026 Microsoft and Omdia study, 42% of security alerts go uninvestigated, increasing the risk of missed threats.
By automating repetitive investigations, reducing unnecessary escalations, and resolving more alerts at Tier 1. This helps teams handle higher workloads while making better use of existing resources.
A healthcare-focused MSSP reduced phishing triage time by 76%, from 30–40 minutes to just 4–7 minutes, after implementing ANY.RUN’s Interactive Sandbox, TI Lookup, and TI Feeds.
It provides evidence of actual threat activity, helping analysts distinguish malicious behavior from false positives faster. This reduces manual investigation time and allows experienced specialists to focus on complex incidents.
Key metrics include investigation cost per alert, mean time to detect (MTTD), mean time to respond (MTTR), Tier 1 resolution rate, escalation rate, and SLA adherence. Together, they help measure efficiency gains and their impact on SOC resources.
The post 76% Faster Triage: How US SOCs Increase ROI Through Visibility and Automation appeared first on ANY.RUN's Cybersecurity Blog.
Article Link: 76% Faster Triage: How US SOCs Increase ROI