<div>
<div>
<div>
<img alt="" src="https://quointelligence.eu/wp-content/uploads/2020/03/[email protected]" title="" />
</div><div>
<div><p>QuoIntelligence’s Weekly Intelligence Snapshot for the week of<strong> 29 July – 05 August 2020</strong> is now available!</p>
Find the summary below and subscribe to our mailing list at the bottom if you want to receive Weekly summaries and other regular updates from us! Or inquire today to receive a free trial of our full Weekly Intelligence Product, which includes analyst comments, MITRE ATT&CK tags, IOCs, and more!
<div><h2>CYBER</h2>
Incident
Industry impacted: Communication Services, Energy, Government, Health Care, Industrials, Information Technology, Materials, Utilities
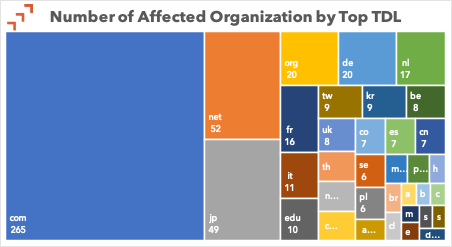
- On Monday, 3 August, a user published a post titled “1800 vulnerable and compromised pulse vpn” on an Russian-speaking underground forum. The post contained a data dump including information of 1,800 Pulse VPN compromised servers vulnerable to CVE-2019-11510, a critical vulnerability that was patched in April 2019 and massively exploited since August 2019 by both e-crime and APT actors.
Current Threat
Industry impacted: ANY
- Researchers at Sophos detailed new techniques implemented by WastedLocker ransomware operators leveraging the Windows memory management feature to evade detection from anti-ransomware solutions.
Threat Actor
Industry impacted: Financials
- QuoIntelligence recently identified at least three new spear phishing campaigns which occurred between May and July 2020, that aligns with the known fake job scheme used by FIN6, and also leverages multiple tools from the Golden Chickens Malware-as-a-Service. While we confirm the campaigns occurred between May and July, they are likely still ongoing.
<div><p><strong>Rollups</strong></p>
Industry impacted: ANY, Government, Health Care, Information Technology
- APT34: Newly Incorporates DNS-over-HTTP To Conduct Cyber Operation
- Spear Phishing Campaign Targeting Aerospace and Defense Shares Similar Tactics to Lazarus Group
- Joint Release from US Government Agencies Attributed Malware Used in Cyberespionage Campaigns to Chinese Government Linked Threat Groups
<div><h2>GEOPOLITICS</h2>
<div><h2><strong>Rollups</strong></h2>
- Australia Releases Cyber Security Strategy 2020
- US Government Observes Increase In Ransomware Attacks Targeting State and Local Government as Election Approache
		</div> <div>
			<div>


			<div>
			<a href="https://quointelligence.eu/weekly-intelligence-bulletin/" rel="noreferrer" target="_blank">About Our Weekly Intelligence Snapshot</a>
		</div><div>


			<div><h2>Join our Newsletter!</h2><div>
Subscribe to our newsletter with your business email to receive intelligence summaries, analytic product updates, and more!
			<div>

					<div></div>
					<div>
						<h2>Thanks! You will soon receive a confirmation email!</h2>
					</div>
					<div>

				<p>
					First Name

				</p>

				<p>
					Last Name

				</p>

				<p>
					Email

				</p>


				<p>
					<a href="https://quointelligence.eu" rel="noreferrer" target="_blank">

						Subscribe
					</a>
				</p>

					</div>


			</div>
		</div>
		</div>


		</div>


		</div>
The post Weekly Intelligence Snapshot – Week 32 appeared first on QuoIntelligence - Our Finished Intelligence, Tailor-made for Your Organization.