CVE-2026-1281 & CVE-2026-1340: Ivanti EPMM Zero-Day Vulnerabilities Enable Unauthenticated RCE
Introduction to Malware Binary Triage (IMBT) Course
Looking to level up your skills? Get 10% off using coupon code: MWNEWS10 for any flavor.
Enroll Now and Save 10%: Coupon Code MWNEWS10
Note: Affiliate link – your enrollment helps support this platform at no extra cost to you.
Ivanti has released emergency security updates after disclosing two critical vulnerabilities (CVE-2026-1281 and CVE-2026-1340) in Ivanti Endpoint Manager Mobile (EPMM) that have been actively exploited as zero-day attacks. Both flaws allow unauthenticated remote code execution, meaning attackers do not need valid credentials to compromise vulnerable systems. One of the vulnerabilities has also been added to CISA’s Known Exploited Vulnerabilities (KEV) catalog, increasing the urgency for affected organizations to act.
What Are CVE-2026-1281 and CVE-2026-1340?
CVE-2026-1281 and CVE-2026-1340 are critical code injection vulnerabilities in Ivanti EPMM, each assigned a CVSS score of 9.8. Successful exploitation allows attackers to execute arbitrary code on the EPMM appliance without authentication.
Both vulnerabilities stem from improper handling of input within specific EPMM features, enabling attackers to inject and run system-level commands. Because no user interaction or credentials are required, exposed systems can be compromised directly over the network.
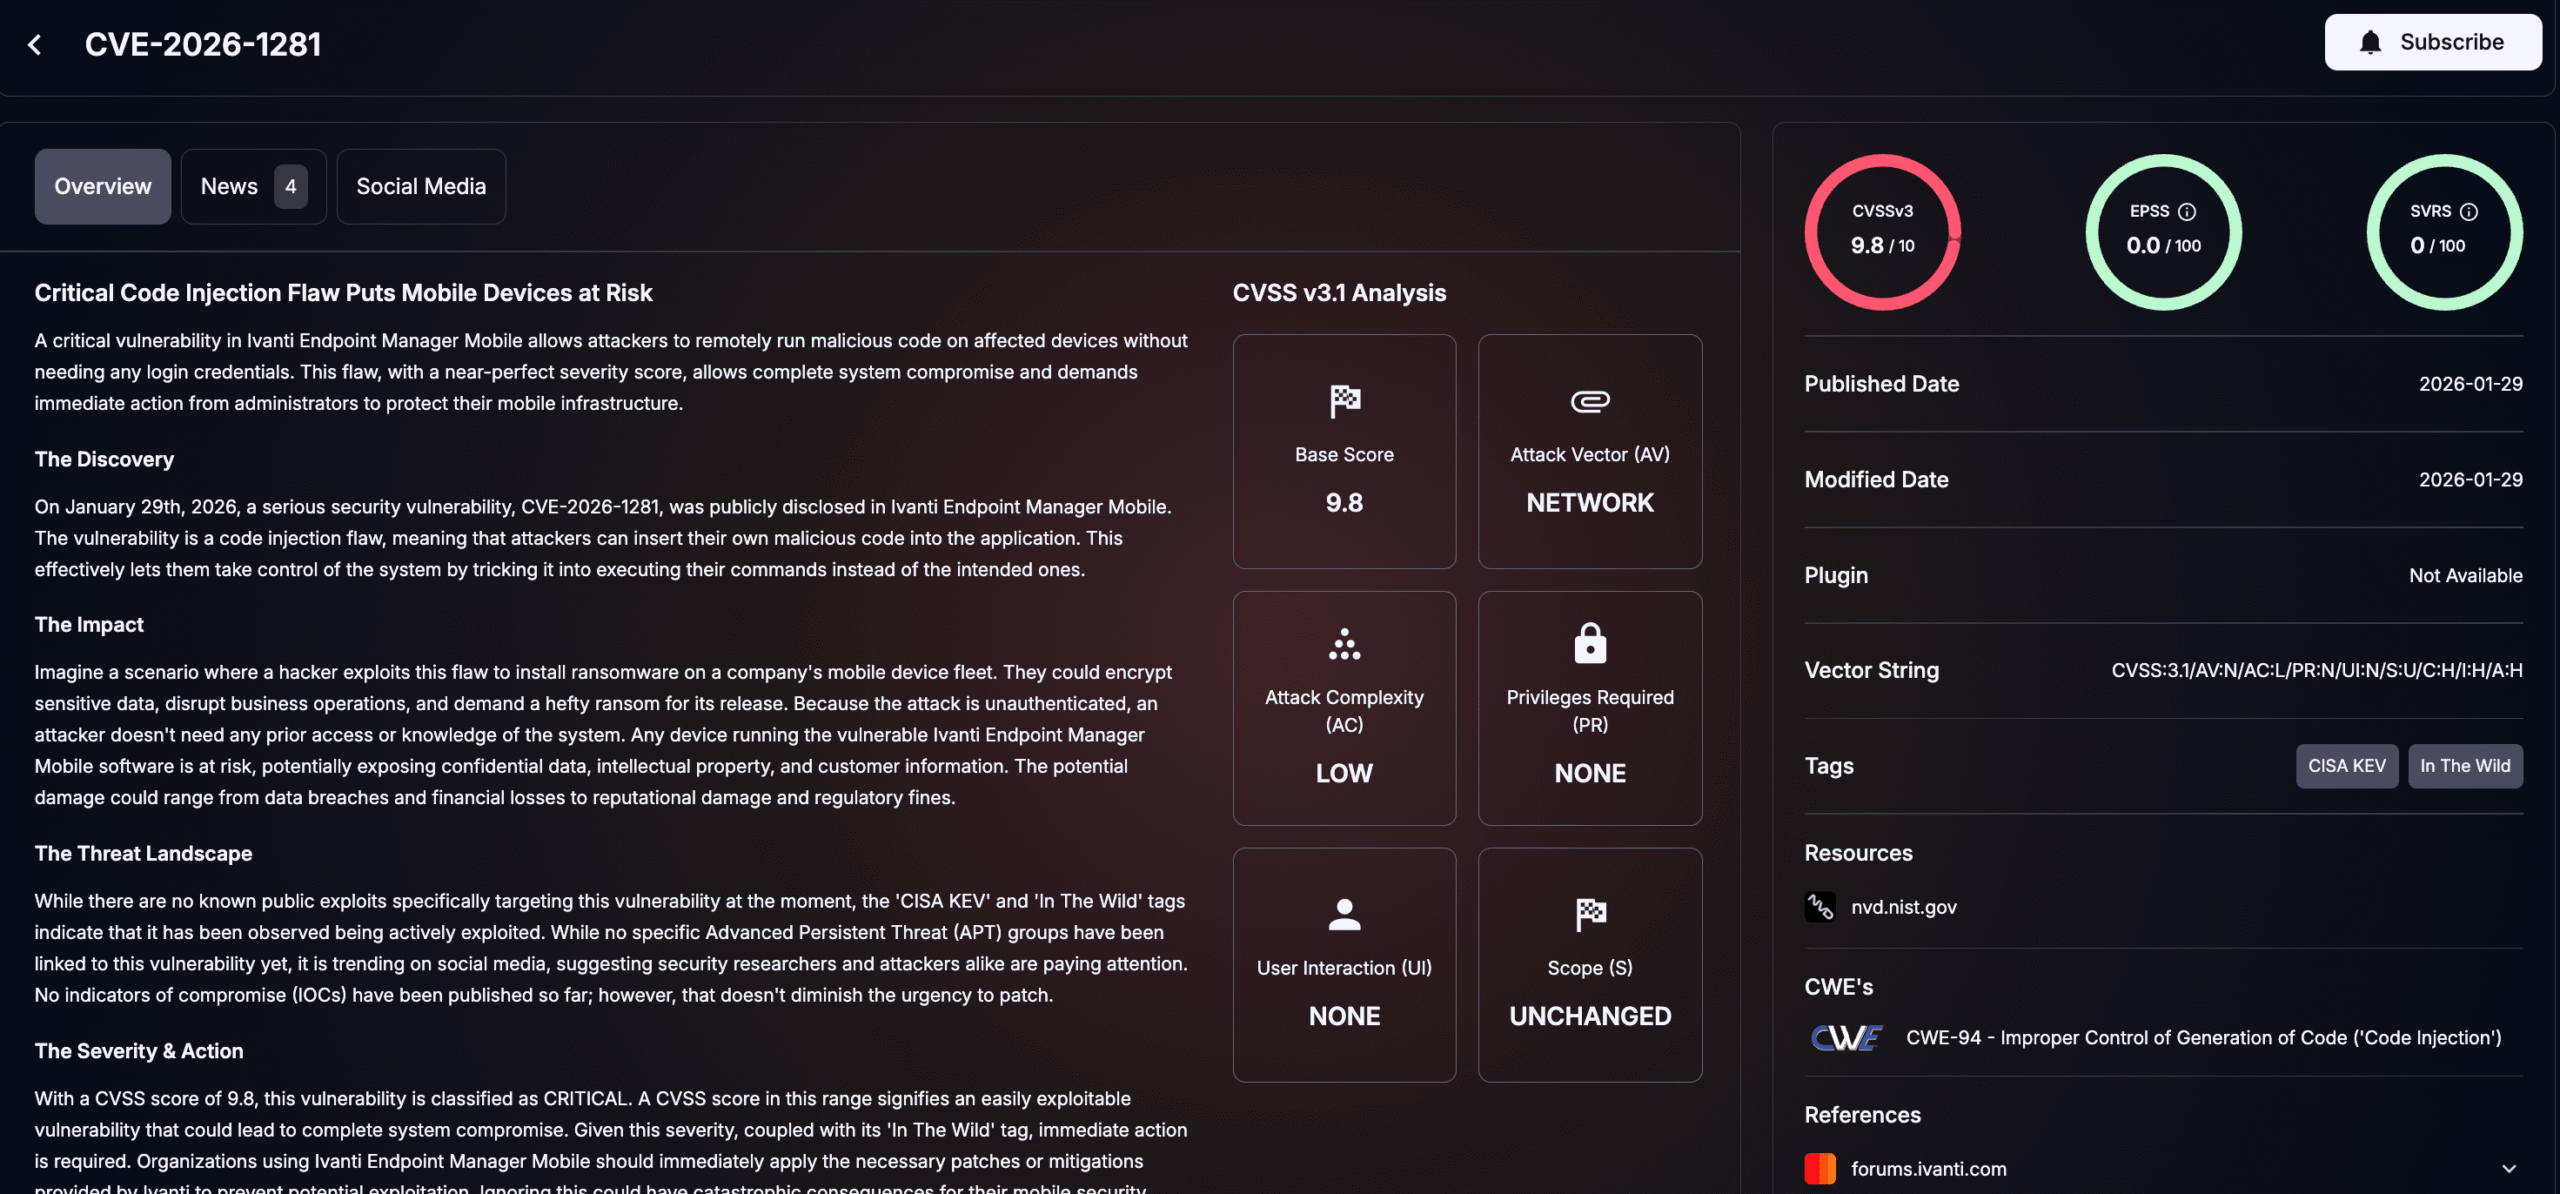
Details of CVE-2026-1281 (SOCRadar Vulnerability Intelligence)
Stay ahead of emerging threats with Vulnerability Intelligence powered by SOCRadar’s Cyber Threat Intelligence module. It continuously tracks new CVEs, threat actor activity, and real-world attack trends, helping security teams prioritize patching based on actual risk, not just severity scores.
Which Ivanti Products and Versions Are Affected?
The vulnerabilities affect Ivanti Endpoint Manager Mobile only. Other Ivanti products, including Ivanti Neurons for MDM, Ivanti Endpoint Manager (EPM), and Ivanti Sentry, are not directly impacted.
Affected versions include:
- EPMM 12.5.0.0, 12.6.0.0, and 12.7.0.0 and earlier
- EPMM 12.5.1.0 and 12.6.1.0 and earlier
Ivanti has released RPM-based interim patches for supported versions. However, these patches do not persist across version upgrades. A permanent fix will be included in EPMM version 12.8.0.0, scheduled for release later in Q1 2026. Full details are available in Ivanti’s official advisory.
How Are These Vulnerabilities Being Exploited?
Ivanti has confirmed a limited number of real-world exploitation cases but noted that detailed threat actor indicators are not yet available. Based on prior investigations of similar EPMM attacks, exploitation typically results in web shell or reverse shell deployment to maintain persistence.
Once compromised, an attacker gains the ability to:
- Execute arbitrary commands on the appliance
- Access sensitive information stored in EPMM
- Potentially move laterally to connected systems and services
Because EPMM appliances are not expected to initiate outbound connections under normal conditions, unusual outbound network activity may also indicate post-exploitation behavior.
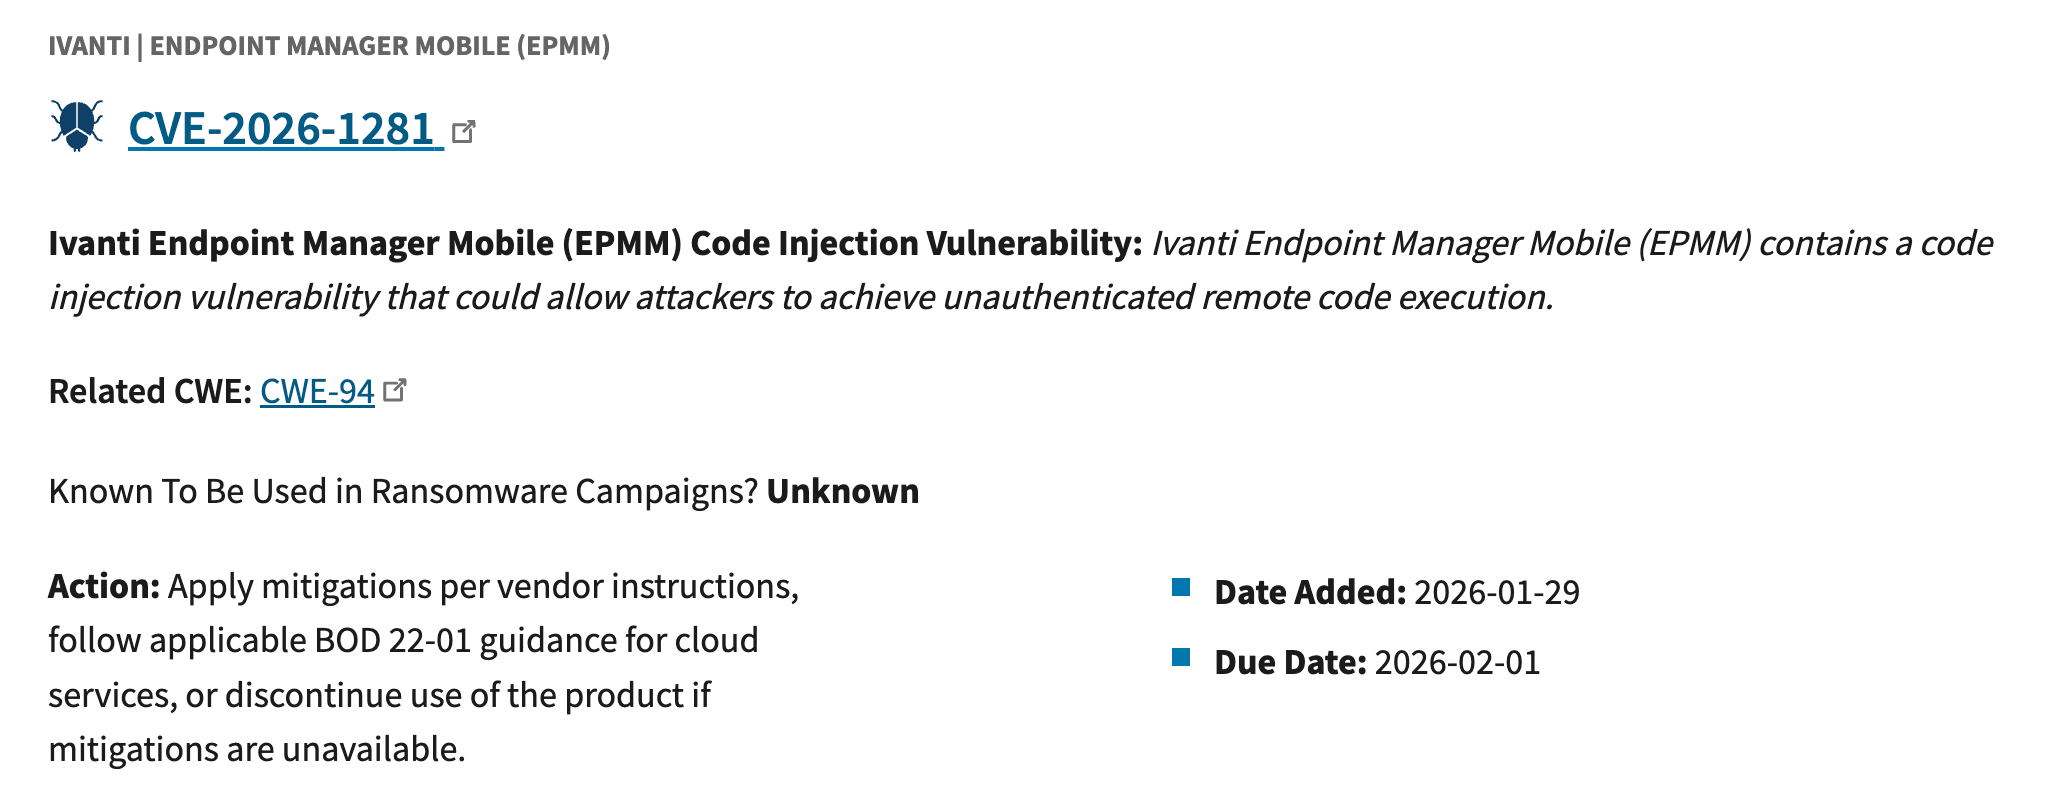
CISA KEV listing for the Ivanti EPMM zero-day
Additionally, CISA has mandated that federal agencies remediate CVE-2026-1281 by February 1, 2026, adding it to the Known Exploited Vulnerabilities (KEV) Catalog.
How Can Organizations Detect Signs of Compromise?
Detection currently relies on behavioral and log-based analysis rather than precise indicators of compromise. Ivanti recommends reviewing Apache access logs located at:
/var/log/httpd/https-access_log
Requests targeting vulnerable endpoints that return 404 HTTP status codes may indicate attempted or successful exploitation. Ivanti has provided the following regex to help identify suspicious entries:
^(?!127.0.0.1:d+.*$).*?/mifs/c/(aft|app)store/fob/.*?404
In addition to log review, organizations should examine:
- Newly created or modified EPMM administrator accounts
- Changes to SSO, LDAP, or authentication settings
- Unexpected pushed applications or policy updates
- Network or VPN configuration changes
Further investigation and forensic guidance is published in Ivanti’s analysis.
What Are the Recommended Remediation and Recovery Steps?
Ivanti strongly advises patching first, followed by a thorough review for compromise. If exploitation is suspected, Ivanti does not recommend attempting to manually clean the appliance.
Preferred recovery options include:
- Restoring EPMM from a known-good backup created before exploitation occurred
- Building a new EPMM appliance and migrating data from the affected system
After recovery, additional security steps should be taken:
- Reset all local EPMM account passwords
- Rotate LDAP, KDC, and service account credentials
- Revoke and replace public certificates used by EPMM
- Review dependent systems, including any connected Sentry deployments, for lateral movement
Turn Exposure Into Actionable Risk Intelligence With SOCRadar
Modern attacks don’t start with alerts; they start with exposure. SOCRadar’s Attack Surface Management (ASM) helps you uncover what’s visible to attackers by continuously mapping internet-facing assets, shadow IT, misconfigurations, and unknown services before they are abused.
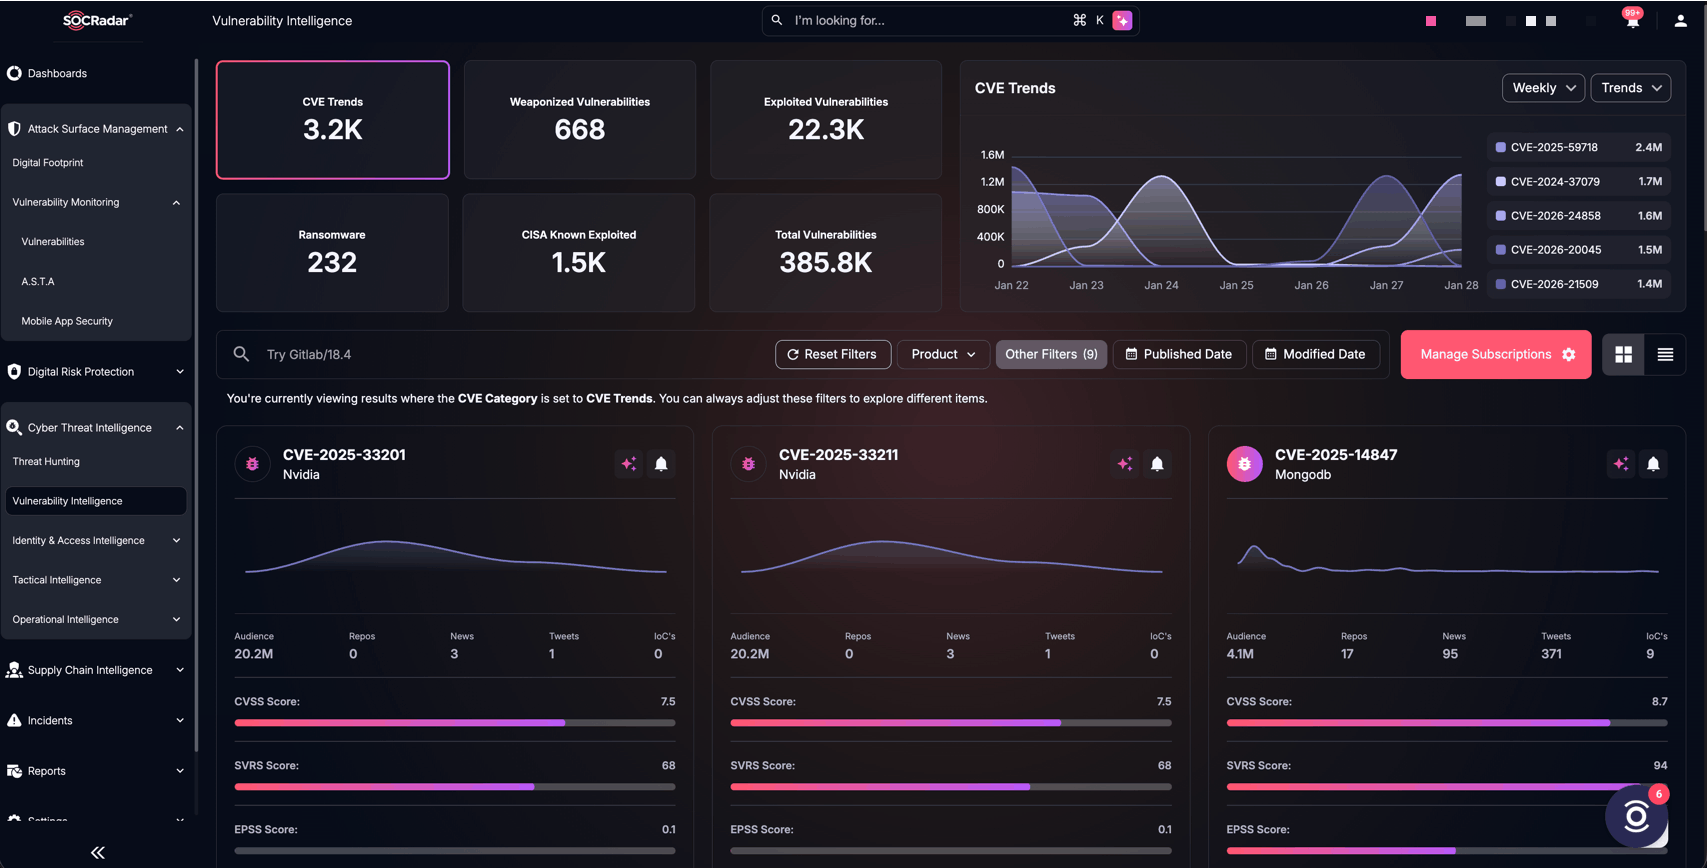
SOCRadar’s Vulnerability Intelligence
Together, ASM and CTI modules enable a risk-driven security approach: discover your external attack surface, identify high-risk vulnerabilities, and prioritize remediation based on real exploitation, not assumptions. The result is faster decisions, reduced attack paths, and stronger protection against emerging threats – without drowning teams in noise.
Article Link: https://socradar.io/blog/cve-2026-1281-1340-ivanti-epmm-0day-rce/